undefined
# Cloud built smarter
> Your 100% AWS-focused company with global ambitions. We tailor our services to meet your compliance and security needs.
Forrict builds and runs AWS environments with total transparency and craftsmanship. We make your cloud, and your team better.
[How we work](/en/how-we-work)[Talk to an expert](mailto:info@forrict.nl)
## We work with the following partners and tools
## Your Cloud, but better.
Whether you’re just starting with Cloud or scaling a fast-growing platform, we help you build a cloud foundation that’s secure, resilient, and ready for tomorrow.
### Landing Zones & Governance
A secure, multi-account AWS foundation built the right way using Well-Architected principles, guardrails, automation, and full transparency.
[Learn more](/en/services/landingzones)
### Managed AWS
We run your AWS so your team can focus on building your product not chasing alarms or compliance updates.
[Learn more](/en/services/managed-aws)
### Cost Optimization
Real insights. Real savings. Real control. We bring clarity to your AWS spend and help you invest in what actually drives the business.
[Learn more](/en/services/Finops)
### Security Assessment
Strengthen the security posture of your AWS infrastructure with comprehensive assessments.
[Learn more](/en/services/Security-assessment)
### Flex Consult
Your on-demand AWS brain: architecture reviews, hands-on support, cost audits, challenging roadmaps whatever you need, when you need it.
[Learn more](/en/services/Flex-consult)
![AWS Select Tier Services Partner]()
Trusted AWS Consulting Partner
## AWS Select Tier Partner
We combine deep AWS expertise with a pragmatic, business-first approach. If it\`s not secure, scalable, and maintainable — we don\`t ship it.
### What we excel at:
Cloud Architecture
Security & Compliance
FinOps & Cost Optimization
Managed Services
Migration & Modernization
## Ready to transform your cloud?
Let's discuss how we can help you achieve your AWS goals
[Get in Touch](mailto:info@forrict.nl)
[How We Work ](/en/how-we-work)
---
# About Forrict
> Forrict specializes in AWS cloud architecture and engineering. Our highly skilled professionals design and implement secure, scalable AWS solutions for Dutch businesses.
## Our story
Forrict was born from a simple idea: Cloud should make businesses stronger, not more dependent.
We saw too many companies trapped in black-box solutions, unclear architectures, and vendors who kept all the knowledge to themselves. So we created a different kind of cloud partner one that shares everything, teaches openly, and designs with long-term independence in mind. Today, we help organizations grow confidently in the cloud, with secure foundations, smart FinOps, and hands-on expertise that truly levels up teams.
## Our Expertise
### Security & Compliance
AVG/GDPR compliance, security architecture, and implementation of AWS security best practices.
### Cloud Architecture
Well-Architected Framework implementation, multi-account strategies, and scalable infrastructure design.
### FinOps & Cost Optimization
Cloud cost management, resource optimization, and financial governance for AWS environments.
### Migration Services
Strategic cloud migration planning and execution with minimal downtime and risk.
### DevOps & Automation
CI/CD pipelines, infrastructure as code (CDK, CloudFormation), and automation solutions.
### Managed Services
24/7 AWS infrastructure management, monitoring, and support for business continuity.
## Why Choose Forrict?
### AWS Certified Experts
Our team holds multiple AWS certifications including Solutions Architect Professional and Security Specialty
### Share by default
We open everything up. Every line of code, every design decision, every diagram, yours to inspect, learn from, and build upon.
### Proven Track Record
Successfully delivered 20+ AWS projects across financial, healthcare, energy, and retail sectors
### Knowledge Transfer
We don't just implement, we ensure your team is empowered to manage and optimize AWS
## Ready to Work Together?
Let's discuss how Forrict can help transform your AWS infrastructure
[ Contact Us ](mailto:info@forrict.nl)
[How We Work](/en/how-we-work)
---
# Getting Started with AWS CDK in TypeScript
> Start using AWS CDK with TypeScript, covering setup, deployment, and best practices
Start using AWS CDK with TypeScript, covering setup, deployment, and best practices
## Why CDK?
Infrastructure as Code (IaC) has changed how teams manage cloud infrastructure. AWS CDK builds on that idea by letting you define infrastructure using real programming languages instead of static templates.
Instead of writing large YAML or JSON files, you model infrastructure using TypeScript constructs, with type safety, refactoring support, and tests.
Learning CDK with TypeScript will transform your infrastructure workflows and enhance your engineering capabilities. With features like:
* Strong typing for catching errors early
* Robust testing capabilities
* Rich ecosystem support
## What is AWS CDK, and Why Should You Learn It?
### What is AWS CDK?
AWS CDK is an open-source framework that lets you define cloud infrastructure using code. Instead of writing verbose JSON or YAML templates, you can use TypeScript to manage resources like:
* S3 buckets
* Lambda functions
* VPCs
* And much more
```
// Example: Creating an S3 bucket with CDK
import * as cdk from 'aws-cdk-lib';
import * as s3 from 'aws-cdk-lib/aws-s3';
new s3.Bucket(this, 'MyBucket', {
versioned: true,
encryption: s3.BucketEncryption.S3_MANAGED,
});
```
### Key Benefits
1. **Simplified Infrastructure Management**
* No more manual setups
* Reduced human error
* Version control for your infrastructure
2. **Reusable Patterns**
* Create custom constructs
* Share across teams
* Maintain consistency
3. **Programming Features**
* Use loops and conditions
* Implement custom logic
* Leverage type safety
> 🚀 **Pro Tip**: Start with simple resources and gradually build up to more complex infrastructure patterns.
## Prerequisites for Getting Started
### Technical Requirements
Before diving in, ensure you have:
📋 **Essential Tools**
* AWS Account (free tier works fine)
* Node.js and npm (latest LTS version)
* AWS CLI configured
📋 **Development Environment**
* VS Code with TypeScrip extensions, or any other editor you like.
* Git for version control
* Terminal access
### Installation Steps
1. **Install Node.js**
```
# Check if Node.js is installed
node --version
# If not, download from nodejs.org
```
2. **Install AWS CDK CLI**
```
npm install -g aws-cdk
# Verify installation
cdk --version
```
3. **Configure AWS CLI**
```
aws configure
# Follow prompts for access key and secret
```
## Step-by-Step: Your First AWS CDK Project in TypeScript
### 1. Project Setup
Create your first CDK project:
```
# Create project directory
mkdir cdk-project
cd cdk-project
# Initialize CDK app
cdk init app --language=typescript
```
Your project structure should look like this:
```
cdk-project/
├── bin/
│ └── cdk-project.ts # Entry point
├── lib/
│ └── cdk-project-stack.ts # Stack definition
├── test/
│ └── cdk-project.test.ts # Tests
├── cdk.json
└── package.json
```
### 2. Creating Your First Stack
Open `lib/cdk-project-stack.ts` and add:
```
import * as cdk from 'aws-cdk-lib';
import { Construct } from 'constructs';
import * as s3 from 'aws-cdk-lib/aws-s3';
export class CdkProjectStack extends cdk.Stack {
constructor(scope: Construct, id: string, props?: cdk.StackProps) {
super(scope, id, props);
// Create an S3 bucket
const bucket = new s3.Bucket(this, 'MyFirstBucket', {
versioned: true,
encryption: s3.BucketEncryption.S3_MANAGED,
removalPolicy: cdk.RemovalPolicy.DESTROY, // For testing only
});
// Output the bucket name
new cdk.CfnOutput(this, 'BucketName', {
value: bucket.bucketName,
description: 'The name of the S3 bucket',
});
}
}
```
### 3. Deployment
Deploy your stack:
```
# Synthesize CloudFormation template
cdk synth
# Deploy to AWS
cdk deploy
```
> ⚠️ **Important**: Always review the changes before deploying:
>
> ```
> cdk diff
> ```
### 4. Testing and Iteration
Add a lifecycle policy to your bucket:
```
const bucket = new s3.Bucket(this, 'MyFirstBucket', {
versioned: true,
encryption: s3.BucketEncryption.S3_MANAGED,
removalPolicy: cdk.RemovalPolicy.DESTROY,
lifecycleRules: [
{
expiration: cdk.Duration.days(365),
transitions: [
{
storageClass: s3.StorageClass.INFREQUENT_ACCESS,
transitionAfter: cdk.Duration.days(30),
},
],
},
],
});
```
> 📚 **Further Reading**: Check out the [AWS CDK Workshop](https://cdkworkshop.com) for hands-on exercises.
F
### Fons Biemans
AWS expert and consultant at Forrict, specializing in cloud architecture and AWS best practices for Dutch businesses.
### Tags
AWS CDK TypeScript Infrastructure as Code Cloud Development
## Stay in the loop
Get AWS insights and tips delivered to your inbox.
### Stay in the loop
Get AWS insights and tips delivered to your inbox.
First name (optional)[Your email address]()Subscribe
## Related Articles
[](/en/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
Apr 14, 2026
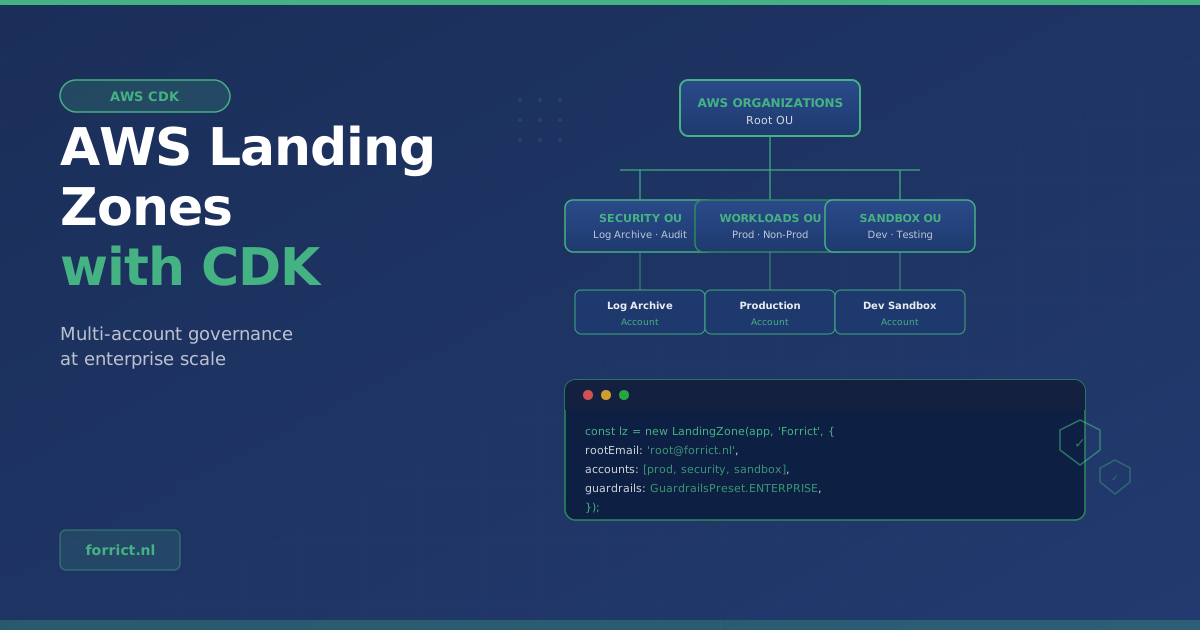
### [AWS Landing Zones with CDK](/en/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
Build secure, scalable AWS landing zones with CDK. Learn multi-account strategy, guardrails, account vending, and why CDK beats Terraform for AWS-native infrastructure.
[Read more](/en/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
---
# AWS Landing Zones with CDK
> Build secure, scalable AWS landing zones with CDK. Learn multi-account strategy, guardrails, account vending, and why CDK beats Terraform for AWS-native infrastructure.

Build secure, scalable AWS landing zones with CDK. Learn multi-account strategy, guardrails, account vending, and why CDK beats Terraform for AWS-native infrastructure.
Your AWS account is not a strategy. Ten unmanaged accounts? That’s a liability waiting to show up in your next audit.
We learned this the hard way. When we started building landing zones for enterprises the pattern was always the same. Inconsistent security baselines. Developers getting accounts with zero guardrails. A networking setup held together by tribal knowledge and a Confluence page nobody’s updated since 2021.
A landing zone fixes this. It’s the foundation that makes governance, security, cost control, and developer velocity work together. But *how* you build that landing zone matters just as much as building one at all.
## Why enterprises need a multi-account strategy
You know what an AWS account is. The question worth asking: why do organizations with 5, 50, or 500 accounts need a formalized approach?
**Blast radius containment.** A misconfigured IAM role in dev shouldn’t touch production data. Account-level isolation is the strongest boundary AWS offers. Stronger than VPCs, stronger than IAM policies. Use it.
**Compliance at scale.** GDPR, SOC 2, NIS2. The regulatory landscape keeps expanding. Manually auditing each account is a losing game. You need guardrails that *prevent* violations, not detectives that find them after the damage is done.
**Cost visibility.** Without proper account structure and tagging enforcement, your FinOps team is flying blind. We’ve seen organizations burn through six figures in unattributed spend because nobody enforced tagging from day one.
**Developer velocity.** This one surprises people. Good governance doesn’t slow teams down. When a developer can self-service a new account that comes pre-configured with networking, logging, and security baselines, they ship faster than the team waiting three weeks for IT to set things up manually. We’ve seen this firsthand at clients: proper account vending turned a multi-week process into minutes.
## Key components of a landing zone
Every enterprise landing zone needs these building blocks, regardless of tooling choice.
### 1. Account vending
Automated account creation with pre-configured baselines. A developer requests a workload account, and within minutes gets:
* An account in the correct OU with appropriate SCPs applied
* VPC with standardized CIDR ranges connected to Transit Gateway or access to a Shared VPC
* CloudTrail, GuardDuty, Config, and Security Hub enabled
* IAM Identity Center access configured
* Budget alerts set
No tickets. No waiting. No manual setup where someone forgets a step.
We treat account vending as an internal product, not a one-off project. It needs versioning, testing, and a backlog. The teams consuming accounts are your users, and their experience matters.
### 2. Guardrails: SCPs and Config Rules
Service Control Policies are your first line of defense. They define what *can’t* happen, regardless of IAM permissions:
* Prevent disabling CloudTrail or GuardDuty
* Restrict deployments to approved regions (`eu-west-1`, `eu-central-1`, critical for GDPR)
* Block public S3 buckets and unencrypted EBS volumes
* Require specific tags on all resources
AWS Config rules complement SCPs by detecting drift continuously. Together: preventive *and* detective controls.
Our advice? Start opinionated. Lock things down. It’s much easier to relax a guardrail for a legitimate use case than to retroactively enforce one after teams have built around its absence.
### 3. Networking
Transit Gateway as the backbone, connecting workload VPCs to shared services and on-premises networks. The key decisions:
* Hub-and-spoke vs. or Shared VPC’s
* Centralized vs. distributed egress
* DNS resolution strategy (Route 53 Resolver rules)
* Network Firewall placement
Get networking wrong and everything else suffers. This is consistently where we see the most technical debt in organizations that grew their AWS footprint organically.
### 4. Identity and access
IAM Identity Center for human access. Federate with your existing IdP (Entra ID, Okta) and define permission sets mapped to organizational roles.
For machine-to-machine: IAM roles with clearly scoped policies. Cross-account access through role assumption. Never long-lived credentials. We’re amazed how many enterprise environments we still find with static access keys older than some of the team members using them.
### 5. Centralized logging and security
A dedicated Log Archive account aggregating:
* CloudTrail organization trails
* VPC Flow Logs
* Config snapshots and compliance history
* GuardDuty and Security Hub findings
A separate Security Tooling account runs your automation: remediation lambdas, SIEM integrations, compliance dashboards. Keep security tooling isolated from the logs it acts on.
## What the docs don’t tell you
We’ve built enough of these to know where the real pitfalls are. What we wish someone had told us earlier.
**Test your landing zone like software.** We use CDK’s assertion testing to validate that constructs produce the expected CloudFormation output. We test SCPs against realistic scenarios. We run `cdk-nag` in CI. Infrastructure code deserves the same quality bar as application code. Most organizations don’t treat it that way, and they pay for it later.
**Don’t ignore day-two operations.** A landing zone that deploys beautifully but can’t be updated safely is a ticking time bomb. Design for incremental updates from the start. CDK’s `cdk diff` and staged rollouts make this manageable, but only if you plan for it.
**FinOps from day one.** Bake cost allocation tags, budget alerts, and anomaly detection into your baseline. Retrofitting cost visibility after 18 months of untagged resources is painful and expensive. We’ve helped clients cut their AWS bill by 30% just by implementing proper tagging and account structure. That’s not optimization, that’s visibility.
**Code ownership is non-negotiable.** This is core to how we work at Forrict. Every line of CDK code we write for your landing zone? You own it. The Git repo, the pipeline, the deployment process, all yours. We don’t create vendor lock-in to ourselves. When we leave, you should be able to maintain and evolve your landing zone independently. That’s freedom through craftsmanship.
## Ready to build your AWS foundation?
A solid landing zone is the difference between an AWS environment that scales with confidence and one that gets more fragile as you grow. The investment pays for itself in security posture, compliance readiness, developer productivity, and cost visibility.
At Forrict, we build landing zones you own completely. No proprietary tools, no managed-service lock-in. Solid CDK code, battle-tested patterns, and the knowledge transfer to run it yourself.
**Want to set up your AWS foundation the right way?** [**Let’s talk.**](https://forrict.nl/en/contact/)
F
### Forrict
AWS expert and consultant at Forrict, specializing in cloud architecture and AWS best practices for Dutch businesses.
### Tags
AWS CDK Landing Zones Multi-Account Cloud Governance Infrastructure as Code
## Free: AWS Cost Optimization Checklist
Get our 20-point checklist to reduce your AWS bill by up to 30%.
### Get your free download
Enter your details to receive the download link.
First name (optional)[Your email address]()Send me the download
## Related Articles
[](/en/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
Apr 21, 2026
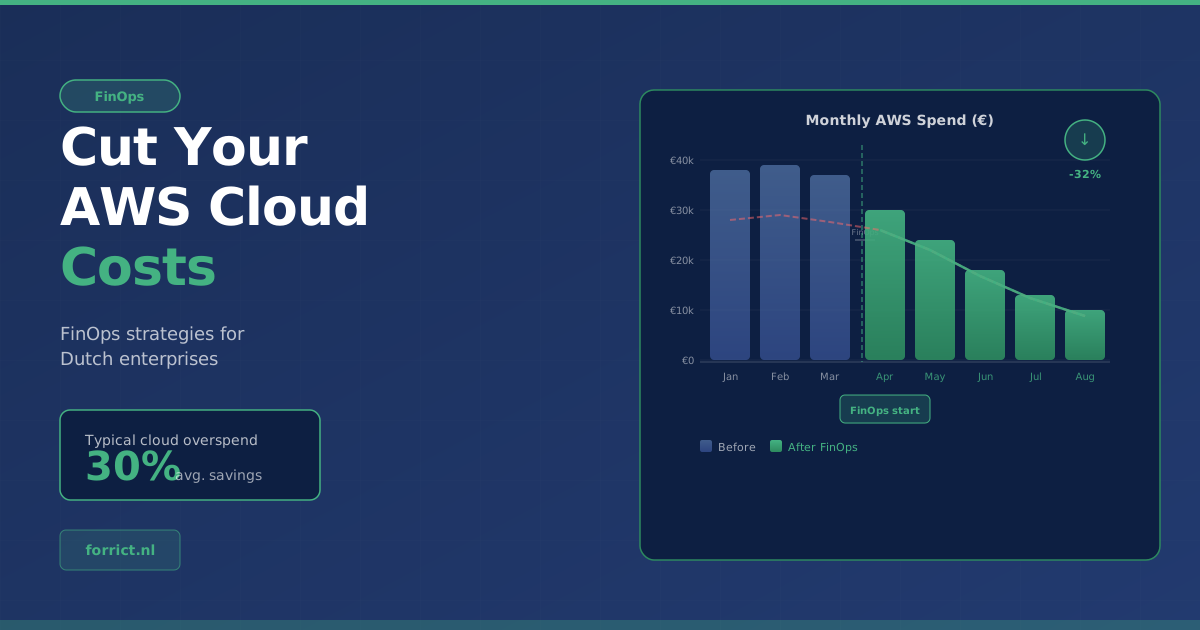
### [FinOps on AWS](/en/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
You're probably overspending on AWS by 30%. Learn the FinOps strategies Dutch enterprises use to cut cloud costs, from zombie cleanup to Savings Plans optimization.
[Read more](/en/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
[](/en/blog/2026-04-28-aws-waf-bot-protection-real-world)
Apr 28, 2026
### [How We Stopped a Bot Attack with AWS WAF](/en/blog/2026-04-28-aws-waf-bot-protection-real-world)
A customer's signup page was under bot attack. Fake accounts, destroyed email reputation, and Tor-masked traffic made traditional blocking useless. Here's how AWS WAF shut it down.
[Read more](/en/blog/2026-04-28-aws-waf-bot-protection-real-world)
[](/en/blog/2026-05-05-aws-well-architected-reviews-health-check)
May 5, 2026
### [AWS Well-Architected Reviews](/en/blog/2026-05-05-aws-well-architected-reviews-health-check)
Your AWS architecture has drifted, you just don't know how far. A Well-Architected Review finds the gaps before they become incidents. Here's what to expect.
[Read more](/en/blog/2026-05-05-aws-well-architected-reviews-health-check)
---
# FinOps on AWS
> You're probably overspending on AWS by 30%. Learn the FinOps strategies Dutch enterprises use to cut cloud costs, from zombie cleanup to Savings Plans optimization.

You're probably overspending on AWS by 30%. Learn the FinOps strategies Dutch enterprises use to cut cloud costs, from zombie cleanup to Savings Plans optimization.
**You’re probably overspending on AWS by 30%. Here’s how we help clients fix it.**
We ran a cost review for a small-size Dutch company last quarter. They were spending €15K/month on AWS. Within six weeks, we cut that by €4K/month, and most of the changes were embarrassingly simple.
Cloud waste doesn’t come from a single bad decision. It’s a thousand small ones compounding over time. An engineer picks m5.xxlarge because it worked last project. A test environment stays running over the weekend. An old snapshot lingers because nobody knows if it’s still needed. Multiply that across fifty teams, and you’ve got a serious budget leak.
According to Flexera’s State of the Cloud Report, enterprises waste roughly 30% of their cloud spend. For Dutch enterprises running €200K-500K/month on AWS, that’s real money. And most of it is fixable without touching a single line of application code.
## Nobody owns the bill
AWS pricing is genuinely complex. Over 300 services, each with their own pricing dimensions: per hour, per GB, per request, per million API calls. But complexity isn’t the root cause of overspending. Lack of ownership is.
We see the same three patterns in almost every engagement:
1. **No tagging strategy.** Without consistent resource tags, costs can’t be attributed to teams or projects. The AWS bill is just one big number that nobody feels responsible for.
2. **Dev/test running 24/7.** That staging cluster running nights and weekends? It’s burning 65% of its budget on empty hours.
3. **Default instance sizes.** Engineers default to what worked before. Nobody checks whether t3.medium handles the actual load just fine.
These aren’t engineering failures. They’re organizational gaps. And they need organizational solutions.
## Quick wins: where the easy money is
Before we talk about culture change (stay with us, we’ll keep it practical), here are the moves that deliver savings fast.
### Kill the zombies
Every AWS account has them. Unattached EBS volumes. Idle Elastic IPs. Forgotten load balancers. Snapshots from instances deleted months ago. AWS won’t clean these up for you. They’ll just keep billing.
Orphaned resources are both a security risk and a money drain, and they’re surprisingly common, even in well-managed environments. We put together a free script that surfaces the most common offenders in minutes. \[Grab it here →]
A systematic zombie sweep typically saves 5-15% of total spend. That’s the kind of return where you wonder why you didn’t do it sooner.
### Right-size your compute
Gartner estimates 40% of cloud instances are at least one size larger than the workload requires. AWS Compute Optimizer can show you exactly where.
But right-sizing isn’t just about going smaller. Sometimes you need a different instance family entirely. CPU-bound workloads belong on c5 or c7g, not general purpose m5. Data-heavy applications might need r5. And Graviton-based instances (m7g, c7g, r7g) deliver roughly 20% better price-performance across the board. Same workload, lower bill.
| Optimization | Typical Savings | Effort |
| ------------------------ | ----------------------------- | --------------------------------- |
| Zombie resource cleanup | 5-15% of total spend | Low, scripted audit |
| Instance right-sizing | 10-30% on compute | Medium, requires utilization data |
| Savings Plans (baseline) | 25-40% on committed workloads | Medium, commitment analysis |
| Non-prod scheduling | Up to 65% on dev/test compute | Low, Instance Scheduler setup |
### Commit where it makes sense
Savings Plans and Reserved Instances can save up to 72% versus On-Demand pricing. The catch: you’re committing to a usage level for 1-3 years. That scares people.
It shouldn’t. The trick is to commit conservatively. Look at your usage floor, the baseline you hit even at 3 AM on a Sunday. Cover that with Compute Savings Plans for maximum flexibility. Layer in EC2 Instance Savings Plans only for workloads you’re confident won’t change. Keep the variable portion On-Demand or Spot.
We’ve seen enterprises leave six figures on the table annually because they were afraid to commit. Don’t be one of them.
### Schedule non-production environments
This one’s almost too easy. That acceptance environment doesn’t need to run at 2 AM on Sunday. AWS Instance Scheduler lets you define operating windows (Monday to Friday, 07:00-19:00) and automatically stops and starts EC2 and RDS instances.
For a typical dev/test setup, that’s 65% fewer running hours. Across multiple environments, the savings compound quickly.
## Structural wins: the changes that actually stick
Quick wins are satisfying. But if the same waste patterns creep back every quarter, you haven’t solved the problem.
### Tags are everything
Tags are the foundation of cloud cost management. Without them, you literally cannot answer “which team is spending what on which project.”
At minimum, every resource needs:
* **Environment** — production, staging, development
* **Team/Owner** — who’s accountable
* **Project/Cost Center** — where to allocate the cost
* **Application** — what system it belongs to
Don’t make tagging optional. Use AWS Organizations SCPs and Tag Policies to enforce compliance at deploy time, or Inherit them from the AWS Account. Set tagging rules in the CDK and Terraform templates, so teams can’t deploy untagged resources even if they try.
### Make costs visible to the people spending them
Once tagging is solid, use AWS Cost and Usage Reports (CUR) to build team-level dashboards. When engineering leads see their team’s AWS spend updating daily, not buried in a monthly finance PDF, behaviour changes on its own.
This isn’t about blame. It’s about ownership. Teams that see their costs make better architecture decisions.
### The FinOps maturity path
The FinOps Foundation breaks this into three stages, and it’s a useful mental model:
* **Crawl:** Visibility. Tagging, Cost Explorer dashboards, a spending baseline.
* **Walk:** Active optimization. Savings Plans purchased, monthly right-sizing reviews, automated scheduling. Cost KPIs per team.
* **Run:** Cost as an engineering metric. Teams factor cost into every architecture decision. Unit economics (cost per transaction, cost per customer) drive optimization.
Most Dutch enterprises we work with are between Crawl and Walk. That’s fine. The biggest savings happen in that exact transition.
## Why this hits different in the Netherlands
The Netherlands leads Europe in cloud adoption. CBS data shows 65-70% of Dutch enterprises use cloud services, compared to an EU average of around 45%. More cloud adoption means more spending, and more potential waste at scale.
On top of that, the regulatory landscape adds cost pressure. GDPR, NIS2 for critical infrastructure, DORA for financial services. Every compliance tool, audit log, and security scan running in your AWS environment has a price tag. If you’re not managing these costs deliberately, they spiral fast.
And then there’s the sovereignty question. Many Dutch enterprises require EU-based hosting, typically AWS eu-west-1 (Ireland) or eu-central-1 (Frankfurt). Cross-region data transfer isn’t free. Regional pricing varies. These are real cost dimensions that deserve deliberate optimization.
## How we do FinOps at Forrict
We don’t do one-time cost audits. We’ve seen what happens: savings last a quarter, then drift back to baseline because nobody’s watching.
Our approach is continuous FinOps embedded in your AWS operations:
1. **Baseline assessment.** We analyze current spend, identify waste, and build a prioritized roadmap. Not a 50-page PDF gathering dust, a ranked action list with expected savings per item.
2. **Quick wins first.** Zombies, right-sizing, scheduling. These typically deliver 20-30% savings within the first month and build momentum for the structural work.
3. **Structural implementation.** Tagging strategy, cost allocation, Savings Plans purchasing, automated enforcement. All built into your Landing Zone so they’re on by default.
4. **Continuous optimization.** Monthly cost reviews, anomaly alerts, architecture recommendations. FinOps isn’t a project that ends. It’s a practice that compounds.
Everything we build, you own. The dashboards, the automation, the CDK, Terraform modules. It’s your code, in your repository. We’re not locking you into a cost management platform. We’re building the capability inside your organization.
## What the numbers look like
For a mid-size Dutch enterprise spending €200K-500K/month on AWS:
| Optimization Area | Monthly Savings |
| --------------------------------- | ----------------------- |
| Zombie cleanup + scheduling | €20K-75K |
| Right-sizing + Graviton migration | €20K-100K |
| Savings Plans optimization | €50K-150K |
| **Combined first-year impact** | **€300K-1.2M annually** |
These ranges align with what AWS FinOps practitioners consistently report across mid-size European enterprises. Your mileage will vary, but the direction is always the same.
##
## **Not sure where to start?**
Book a free 30-minute AWS Waste Scan. Share read-only Cost Explorer access beforehand and we’ll come prepared with your three biggest savings opportunities — no fluff, no sales pitch. [Book your free Waste Scan](https://forrict.nl/en/contact/)
***
*Forrict is an AWS Select Tier Partner based in the Netherlands, specializing in Landing Zones, managed AWS operations, and FinOps. We help Dutch enterprises build scalable, secure cloud environments and keep the costs under control.*
F
### Forrict
AWS expert and consultant at Forrict, specializing in cloud architecture and AWS best practices for Dutch businesses.
### Tags
FinOps AWS Cost Optimization Cloud Costs Savings Plans Dutch Enterprise
## Stay in the loop
Get AWS insights and tips delivered to your inbox.
### Stay in the loop
Get AWS insights and tips delivered to your inbox.
First name (optional)[Your email address]()Subscribe
## Related Articles
[](/en/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
Apr 14, 2026
### [AWS Landing Zones with CDK](/en/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
Build secure, scalable AWS landing zones with CDK. Learn multi-account strategy, guardrails, account vending, and why CDK beats Terraform for AWS-native infrastructure.
[Read more](/en/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
[](/en/blog/2026-04-28-aws-waf-bot-protection-real-world)
Apr 28, 2026
### [How We Stopped a Bot Attack with AWS WAF](/en/blog/2026-04-28-aws-waf-bot-protection-real-world)
A customer's signup page was under bot attack. Fake accounts, destroyed email reputation, and Tor-masked traffic made traditional blocking useless. Here's how AWS WAF shut it down.
[Read more](/en/blog/2026-04-28-aws-waf-bot-protection-real-world)
[](/en/blog/2026-05-05-aws-well-architected-reviews-health-check)
May 5, 2026
### [AWS Well-Architected Reviews](/en/blog/2026-05-05-aws-well-architected-reviews-health-check)
Your AWS architecture has drifted, you just don't know how far. A Well-Architected Review finds the gaps before they become incidents. Here's what to expect.
[Read more](/en/blog/2026-05-05-aws-well-architected-reviews-health-check)
---
# How We Stopped a Bot Attack with AWS WAF
> A customer's signup page was under bot attack. Fake accounts, destroyed email reputation, and Tor-masked traffic made traditional blocking useless. Here's how AWS WAF shut it down.

A customer's signup page was under bot attack. Fake accounts, destroyed email reputation, and Tor-masked traffic made traditional blocking useless. Here's how AWS WAF shut it down.
A customer called us on a Friday. Their signup page was being hammered by bots. Hundreds of fake accounts were being created every hour, each one using a real person’s email address. Their system was dutifully sending welcome emails to all of them.
The result? Their email sender reputation was tanking. Fast. They were days away from getting their domain blacklisted and their AWS SES access suspended. That’s not a theoretical risk, SES will shut you down if your bounce and complaint rates cross the threshold.
They needed it stopped, Now!
## The problem with traditional defences
The obvious first move is IP-based blocking. Identify the suspicious sources, block them, move on. Simple.
Except some of these bots were routing through the Tor network. Every request came from a different exit node. Block one IP, another one takes its place seconds later. It’s a game you can’t win with rate limiting and IP blacklists alone.
The bots weren’t sophisticated in what they did:
* create account,
* trigger email,
* repeat
but they were very effective at hiding where they came from. Traditional IP-based controls were useless.
## Why this was more dangerous than it looked
On the surface, fake signups sound like a nuisance. Annoying, sure. But dangerous?
Yes. Here’s why.
**Email sender reputation is fragile.** When your domain sends hundreds of emails to addresses whose owners never signed up, those people mark them as spam. Mailbox providers notice. Your domain reputation score drops. Legitimate emails, order confirmations, password resets, invoices, start landing in spam folders. Or get blocked entirely.
**AWS SES has hard limits.** Amazon monitors your bounce rate, complaint rate, and sending patterns. Cross the line and SES puts your account under review. Cross it further and they suspend sending entirely. For a business that depends on transactional email, that’s an outage.
**It escalates quickly.** Bot attacks don’t taper off. They accelerate. Every hour of inaction means more fake accounts, more bounced emails, and more reputation damage to undo. Recovery from a blacklisted domain takes weeks. Sometimes months.
## AWS WAF: the right tool for the job
We deployed AWS WAF in front of their application. WAF sits at the edge, inspecting HTTP requests before they reach your backend. It’s native AWS, integrates with CloudFront, ALB, and API Gateway, and gives you granular control over what traffic gets through.
For this engagement, we focused on three things:
**Managed rule groups.** AWS WAF comes with curated rule sets maintained by AWS and vetted third parties. These include rules specifically designed to identify and block known bad actors, including traffic originating from anonymising networks. We activated the relevant managed rules and immediately started filtering the most obvious bot traffic.
**Behavioural pattern matching.** Beyond known-bad IPs, we configured rules to detect the patterns these bots exhibited. The signup requests had characteristics that distinguished them from legitimate user behaviour. WAF let us define rules that matched those patterns without disrupting real users.
**Rate-based rules.** Even with Tor, the volume of requests from individual exit nodes exceeded what any legitimate user would generate. Rate-based rules added another layer, automatically blocking sources that exceeded reasonable thresholds within a given time window.
The combination worked. Within hours, fake signups dropped to near zero.
## The outcome
| Metric | Before | After |
| ----------------------- | ----------------- | ------------------------- |
| Fake signups per hour | Hundreds | Near zero |
| SES bounce rate | Dangerously high | Within safe thresholds |
| Email sender reputation | Degrading rapidly | Stabilised and recovering |
| Legitimate user impact | None | None |
The customer’s email flow was restored. SES stayed active. Real users never noticed a thing.
## Beyond the immediate fix
Stopping the attack was step one. But bot attacks don’t happen once. They come back. Often smarter.
AWS WAF isn’t a set-and-forget tool. It needs monitoring and tuning. We configured logging via WAF’s integration with CloudWatch to track blocked requests, identify new patterns, and adjust rules as attacker behaviour evolves.
For broader security visibility, we also recommended the customer integrate GuardDuty and Security Hub into their monitoring stack. GuardDuty catches unusual activity at the infrastructure level, compromised instances, anomalous API calls, reconnaissance patterns. Security Hub aggregates findings from WAF, GuardDuty, and other sources into a single compliance-aware dashboard.
Together, these three services create a layered defence:
| Layer | Service | What it covers |
| ---------------------- | ------------ | --------------------------------------------------- |
| **Edge protection** | AWS WAF | HTTP-level filtering, bot mitigation, rate limiting |
| **Threat detection** | GuardDuty | Infrastructure threats, anomalous behaviour |
| **Posture management** | Security Hub | Aggregated findings, compliance dashboards |
No single tool covers everything. But stacked correctly, they cover each other’s blind spots.
## The NIS2 angle
If you’re operating in the EU, bot mitigation isn’t just good practice. It’s becoming a compliance requirement.
NIS2, the EU’s updated directive on network and information security, mandates that organisations in essential and important sectors implement appropriate measures against cyber threats. Bot attacks that compromise email infrastructure, create fraudulent accounts, or disrupt service availability fall squarely within that scope.
Having a documented, automated response capability (like WAF with managed rules and monitoring) demonstrates the kind of “appropriate technical measures” NIS2 expects. It’s not the whole compliance picture, but it’s a meaningful part of it.
## When things go wrong, speed matters
This engagement reinforced something we see again and again: the difference between a minor incident and a serious one is response time.
The customer’s email reputation was already damaged when they called us. Another week of inaction and they’d have been looking at a blacklisted domain and suspended SES access, with cascading effects on their entire business communication.
We had WAF deployed and filtering traffic within hours. Not because the technology is magic, but because we’ve done this before. We knew which rules to activate, how to configure them without blocking legitimate users, and how to validate the results under pressure.
That’s what you get from a team that lives in AWS every day.
## Don’t wait for the attack
Most organisations think about bot protection after the bots arrive. By then, the damage is already accumulating. WAF rules that take an hour to configure during normal operations take the same hour during an incident, but with a lot more stress and a lot less margin for error.
If you’re running signup flows, payment forms, or any publicly exposed application on AWS, the question isn’t whether bots will find it. It’s when.
**We help you respond to threats fast and prevent the next one.**
[Talk to us about securing your AWS environment →](https://forrict.nl/en/contact/)
F
### Forrict
AWS expert and consultant at Forrict, specializing in cloud architecture and AWS best practices for Dutch businesses.
### Tags
AWS WAF Bot Protection Cloud Security NIS2
## Stay in the loop
Get AWS insights and tips delivered to your inbox.
### Stay in the loop
Get AWS insights and tips delivered to your inbox.
First name (optional)[Your email address]()Subscribe
## Related Articles
[](/en/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
Apr 14, 2026
### [AWS Landing Zones with CDK](/en/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
Build secure, scalable AWS landing zones with CDK. Learn multi-account strategy, guardrails, account vending, and why CDK beats Terraform for AWS-native infrastructure.
[Read more](/en/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
[](/en/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
Apr 21, 2026
### [FinOps on AWS](/en/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
You're probably overspending on AWS by 30%. Learn the FinOps strategies Dutch enterprises use to cut cloud costs, from zombie cleanup to Savings Plans optimization.
[Read more](/en/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
[](/en/blog/2026-05-05-aws-well-architected-reviews-health-check)
May 5, 2026
### [AWS Well-Architected Reviews](/en/blog/2026-05-05-aws-well-architected-reviews-health-check)
Your AWS architecture has drifted, you just don't know how far. A Well-Architected Review finds the gaps before they become incidents. Here's what to expect.
[Read more](/en/blog/2026-05-05-aws-well-architected-reviews-health-check)
---
# AWS Well-Architected Reviews
> Your AWS architecture has drifted, you just don't know how far. A Well-Architected Review finds the gaps before they become incidents. Here's what to expect.

Your AWS architecture has drifted, you just don't know how far. A Well-Architected Review finds the gaps before they become incidents. Here's what to expect.
You launched on AWS two years ago. The architecture was solid. Security was tight, costs were reasonable, and the team knew every moving part.
Fast forward to today. Three teams deploy independently. Someone spun up oversized instances “temporarily” six months ago. Your disaster recovery plan lives on a Confluence page nobody has opened since the initial build. And that S3 bucket? Public read access since a demo in Q2.
Nobody plans to build a mess. It just accumulates.
## What the Well-Architected Framework actually is
We run Well-Architected Reviews regularly for Dutch enterprises, and what surprises most teams is that the framework is not a theoretical checklist. It’s a structured set of hard questions designed to surface the things you’ve been too busy to look at.
AWS organizes it around six pillars. You’ve probably seen the list before. But listing pillars is cheap. The value is in the questions each one forces you to answer honestly.
**Operational Excellence** Can your team respond to incidents without heroics? Are deployments automated and repeatable, or does someone SSH into a box at 2 AM? Do you learn from failures, or just fix and move on?
**Security** Who can access what, and how do you know? Is data encrypted at rest and in transit? Could you detect a breach right now, not tomorrow, not after someone notices something weird in CloudWatch?
**Reliability** What happens when a component fails? Have you actually tested failover, or are you hoping the runbook from 2024 still works? Can you scale without manual intervention?
**Performance Efficiency** Are you using the right resource types? When was the last time anyone checked whether those instance families still make sense? Are you running containers on oversized EC2 when Fargate would be half the cost?
**Cost Optimization** Do you know what each team spends, and why? Are you paying for resources nobody uses? Is your tagging strategy real, or a spreadsheet someone filled in once?
**Sustainability** Are you minimizing wasted compute? Could you run the same workload on fewer resources with smarter architecture choices?
Each pillar includes dozens of specific questions. They’re designed to find blind spots, the assumptions your team makes because nobody has verified them recently.
## Why architectures drift
No one wakes up and decides to build a fragile, expensive, insecure environment. Drift is quieter than that.
A feature ships under deadline pressure. The team skips the architecture review because “it’s just a small change.” Multiply that by fifty deployments across three squads over eighteen months. Now your environment looks nothing like what was originally designed, and nobody can pinpoint the moment it went wrong.
What we see most often:
| Finding | What happens in practice |
| ------------------------------ | -------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **No DR testing** | The disaster recovery plan exists. It was written during the initial build. It has never been executed. When the day comes, nobody knows if it works. Hope is not a recovery strategy. |
| **Manual deployments** | One team automated. Two others still deploy by hand. It’s only a matter of time before a manual push introduces something exciting into production. |
| **Over-provisioned resources** | That `m5.4xlarge` was sized for peak load that happened once. It runs at 12% CPU daily. Nobody downsized it because “it works.” It does, and it burns money doing it. |
| **Missing encryption** | Data at rest is encrypted in production but not in staging. Staging has production data in it. You see the problem. |
| **No cost allocation** | The AWS bill arrives. It’s higher than last month. Nobody can explain why with confidence. |
These aren’t edge cases. These are the most common findings across the enterprises we review.
## How we run a Well-Architected Review
A review is not a checkbox exercise. It’s a structured deep dive into your workloads against the six pillars. No 200-page PDF that collects dust. Actual findings you can act on Monday morning.
### Discovery
We start by understanding your landscape. What workloads are running? What’s business-critical? Who deploys what, and how? What does your team topology look like?
This isn’t about auditing your team. It’s about understanding context so the findings land as actionable recommendations, not abstract advice.
### Workload analysis
We assess your architecture against the framework using the AWS Well-Architected Tool and Trusted Advisor. But the tooling is just the starting point. The real value is engineers sitting with your team, reviewing CDK and Terraform configurations, deployment pipelines, monitoring setup, IAM policies, networking, and cost structure. Asking the questions each pillar demands. Digging into the answers.
This is not a vulnerability scan. It’s not an automated report. It’s a conversation.
### Findings report
You get a clear, prioritized report. Critical risks separated from medium-term improvements, separated from nice-to-haves.
Each finding states what the issue is, why it matters, and what to do about it. No ambiguity. No consultant-speak. If we can’t explain a finding in plain language, we haven’t understood it well enough ourselves.
### Remediation roadmap
Findings without a plan are just anxiety. We deliver a prioritized roadmap: what to fix first, estimated effort, and the expected impact of each change.
Security gaps and single points of failure go to the top. Cost optimization gets sequenced by savings potential versus implementation effort. You walk away knowing exactly where to start and what to ignore for now.
## What you actually get out of it
**Reduced risk.** You find the single points of failure, the unencrypted data stores, the IAM policies with `*:*` that someone added “temporarily” three years ago. The cost of prevention is a fraction of the cost of a breach or outage. Every CTO knows this intellectually. A review makes it concrete.
**Lower AWS costs.** Over-provisioned instances, unused Elastic IPs, forgotten snapshots, wrong pricing models. They add up faster than most teams realize. We typically see 10-30% savings on compute spend in the first optimization pass. Some teams stare at the numbers and wonder why they waited.
**Stronger compliance posture.** NIS2 is now enforceable in the Netherlands. GDPR audits are getting more granular every cycle. Dutch enterprises face real regulatory pressure to demonstrate security controls, and the window for getting your house in order is closing. A Well-Architected Review maps directly to these frameworks. It gives you documented evidence of your posture, or shows you exactly where the gaps are before a regulator does.
**Faster incident response.** When you know your architecture inside out (what fails, what recovers, what needs manual intervention), your team responds faster. Runbooks are based on reality, not the assumptions from the original build.
**Confidence to scale.** You can’t scale what you don’t understand. A review gives engineering leadership a clear picture of where the architecture stands and what needs to happen before the next growth phase.
## When should you do one?
There’s no wrong time. But some moments make it especially valuable:
* **Before a major migration or expansion.** Know your baseline before you build on top of it.
* **After rapid growth.** If your team doubled or your workload tripled, your architecture almost certainly didn’t keep pace.
* **Annually, as hygiene.** AWS releases new services constantly. What was well-architected two years ago might not be today.
* **After an incident.** Something broke. A review helps you find the other things waiting to break.
* **Ahead of compliance deadlines.** NIS2 is in force. A Well-Architected Review gives you a head start on demonstrating your controls.
## Your architecture has drifted
Your AWS environment is not static. Your business changes, your team changes, AWS itself changes. What was built right eighteen months ago has drifted. The only question is how far.
A Well-Architected Review gives you clarity. Not a sales pitch. Not a theoretical framework. A concrete assessment of where you stand and what to do next.
[Book a Well-Architected Review with Forrict](https://forrict.nl/en/contact/) and find out where your AWS environment actually stands today.
F
### Forrict
AWS expert and consultant at Forrict, specializing in cloud architecture and AWS best practices for Dutch businesses.
### Tags
AWS Well-Architected Architecture Review Cloud Architecture NIS2 Cost Optimization
## Stay in the loop
Get AWS insights and tips delivered to your inbox.
### Stay in the loop
Get AWS insights and tips delivered to your inbox.
First name (optional)[Your email address]()Subscribe
## Related Articles
[](/en/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
Apr 14, 2026
### [AWS Landing Zones with CDK](/en/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
Build secure, scalable AWS landing zones with CDK. Learn multi-account strategy, guardrails, account vending, and why CDK beats Terraform for AWS-native infrastructure.
[Read more](/en/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
[](/en/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
Apr 21, 2026
### [FinOps on AWS](/en/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
You're probably overspending on AWS by 30%. Learn the FinOps strategies Dutch enterprises use to cut cloud costs, from zombie cleanup to Savings Plans optimization.
[Read more](/en/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
[](/en/blog/2026-04-28-aws-waf-bot-protection-real-world)
Apr 28, 2026
### [How We Stopped a Bot Attack with AWS WAF](/en/blog/2026-04-28-aws-waf-bot-protection-real-world)
A customer's signup page was under bot attack. Fake accounts, destroyed email reputation, and Tor-masked traffic made traditional blocking useless. Here's how AWS WAF shut it down.
[Read more](/en/blog/2026-04-28-aws-waf-bot-protection-real-world)
---
# Insights, Guides & Cloud Know-How
> Expert insights on AWS cloud solutions, best practices, and implementation guides for Dutch businesses
We share what we learn, openly, clearly, and without the fluff.
[](/en/blog/2026-05-05-aws-well-architected-reviews-health-check)
May 5, 2026 Cloud Architecture
## [AWS Well-Architected Reviews](/en/blog/2026-05-05-aws-well-architected-reviews-health-check)
Your AWS architecture has drifted, you just don't know how far. A Well-Architected Review finds the gaps before they become incidents. Here's what to expect.
\#AWS Well-Architected #Architecture Review #Cloud Architecture
[Read article ](/en/blog/2026-05-05-aws-well-architected-reviews-health-check)
[](/en/blog/2026-04-28-aws-waf-bot-protection-real-world)
April 28, 2026 Security
## [How We Stopped a Bot Attack with AWS WAF](/en/blog/2026-04-28-aws-waf-bot-protection-real-world)
A customer's signup page was under bot attack. Fake accounts, destroyed email reputation, and Tor-masked traffic made traditional blocking useless. Here's how AWS WAF shut it down.
\#AWS WAF #Bot Protection #Cloud Security
[Read article ](/en/blog/2026-04-28-aws-waf-bot-protection-real-world)
[](/en/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
April 21, 2026 FinOps
## [FinOps on AWS](/en/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
You're probably overspending on AWS by 30%. Learn the FinOps strategies Dutch enterprises use to cut cloud costs, from zombie cleanup to Savings Plans optimization.
\#FinOps #AWS Cost Optimization #Cloud Costs
[Read article ](/en/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
[](/en/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
April 14, 2026 Cloud Infrastructure
## [AWS Landing Zones with CDK](/en/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
Build secure, scalable AWS landing zones with CDK. Learn multi-account strategy, guardrails, account vending, and why CDK beats Terraform for AWS-native infrastructure.
\#AWS CDK #Landing Zones #Multi-Account
[Read article ](/en/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
[](/en/blog/2025-12-22-getting-started-aws-cdk-typescript)
December 22, 2025 Cloud Infrastructure
## [Getting Started with AWS CDK in TypeScript](/en/blog/2025-12-22-getting-started-aws-cdk-typescript)
Start using AWS CDK with TypeScript, covering setup, deployment, and best practices
\#AWS CDK #TypeScript #Infrastructure as Code
[Read article ](/en/blog/2025-12-22-getting-started-aws-cdk-typescript)
Showing 5 of 5 articles
---
# Success Stories
> Discover how we've helped Dutch businesses transform their AWS infrastructure with real success stories and measurable results.
1. [Home](/en/)
2. /
3. Success Stories
Real results from real Dutch businesses. See how we've helped companies transform their AWS infrastructure.
25+
Projects Delivered
40%
Avg Cost Reduction
24/7
Support Available
 AgriTech / IoT
Protix
### [Protix Uses AWS IoT to Build Reliable, Scalable Monitoring for Insect-Based Protein Production](/en/case-studies/protix-aws-iot)
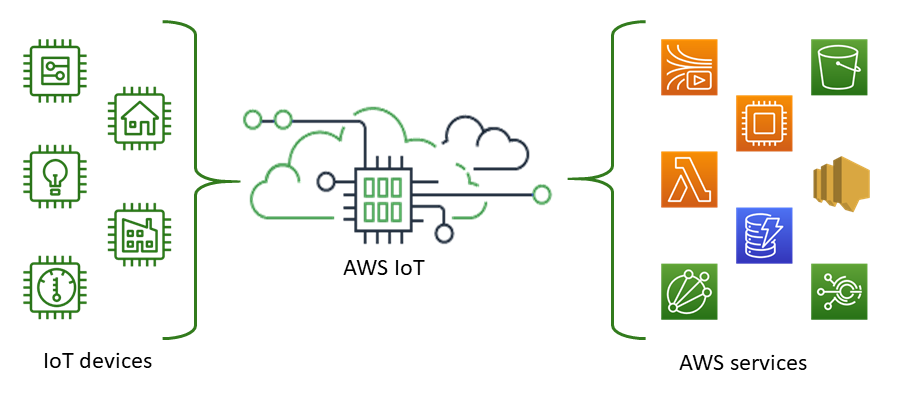
How Forrict implemented a serverless AWS IoT solution to replace Protix's vendor-locked monitoring system, increasing sensor uptime from 1 month to 5-7 years.
Sensor uptime increased from 1 month to 5-7 years
Sensor onboarding reduced to 15 minutes
50% lower measurement costs
IoT AWS IoT Core Serverless
[Read full story ](/en/case-studies/protix-aws-iot)
## Ready to Write Your Success Story?
Let's discuss how we can help transform your AWS infrastructure
[ Contact Us ](mailto:info@forrict.nl)
[How We Work](/en/how-we-work)
---
# Protix Uses AWS IoT to Build Reliable, Scalable Monitoring for Insect-Based Protein Production
> How Forrict implemented a serverless AWS IoT solution to replace Protix's vendor-locked monitoring system, increasing sensor uptime from 1 month to 5-7 years.
## Key Results
Sensor uptime increased from 1 month to 5-7 years
Sensor onboarding reduced to 15 minutes
50% lower measurement costs
1 year historical data retention
Eliminated vendor lock-in

## About the Customer
Protix is a Dutch agritech company headquartered in Den bosch and a first of its kind insect factory in Bergen op Zoom. As a pioneer in insect-based nutrition, Protix grows black soldier fly larvae to produce sustainable protein and lipids from Plant based byproducts. These ingredients replace traditional animal feed components such as fish meal, contributing to circular agriculture and reducing environmental impact.
## Customer Challenge
Protix relied on IoT-based sensors to monitor the temperature and humidity conditions in its R\&D facilities. These sensors operated in a closed, vendor-locked system with a limited set of supported devices, making it difficult to:
* expand sensor coverage,
* integrate new types of sensors,
* access data for advanced analytics.
The hardware frequently broke down, required costly maintenance, and often needed replacement at a rate of one device per month.
Because temperature and humidity are critical for the lifecycle of the black soldier fly, sensor failures created significant business risk. Resulting in production losses and setbacks to ongoing R\&D efforts.
Protix needed a reliable, flexible, cloud-enabled monitoring and control system that could support any LORA Wan sensor type using AWS IoT Core, ensuring production continuity and scalability.
## Our Solution
To address these challenges, Forrict implemented a modern, serverless IoT data pipeline on AWS. The solution was first proven through a proof of concept using Dragino LoRaWAN sensors and gateways that connect directly to AWS IoT Core. This open architecture eliminates vendor lock-in and allows Protix to onboard any type of sensor in the future.
Incoming sensor data flows through AWS IoT Rules, where an AWS Lambda function decodes the payload before routing it to Amazon Timestream, a serverless time-series database. This provides scalable, low-maintenance storage for IoT telemetry. The data is then visualized in real time with Amazon Managed Grafana, enabling Protix engineers and researchers to monitor dashboards and analyze historical trends.
The system currently supports two sensor types, with more planned for future rollout. The architecture is designed for easy extension, allowing new sensors to be added without re-architecting the pipeline.
Forrict manages the end-to-end solution on Protix’s behalf, ensuring operational continuity and minimal maintenance overhead. Protix retains the ability to make minor adjustments, such as onboarding new sensors, while Forrict provides ongoing monitoring, updates, and optimization.
By leveraging serverless AWS services, the system is nearly maintenance-free and enables Protix to retain up to one year of sensor data for analysis. Future enhancements such as single sign-on (SSO) integration and automated alerts/notifications are already under discussion.
## Results and Benefits
The AWS-based solution has transformed Protix’s production monitoring, delivering both operational stability and business value.
* **Sensor uptime increased from 1 month to 5–7 years**, thanks to long-lasting LoRaWAN devices with monitored battery status.
* **Sensor onboarding time dropped to 15 minutes**, enabling rapid expansion across facilities.
* **50% lower measurement costs**, Sensors now allow for multiple measurements per device, reducing per-measurement costs compared to the legacy system.
* **Centralized dashboards** provide visibility across from everywhere
* **Historical data retention** of one year supports both production analysis and R\&D.
* **Reduced downtime risk** through proactive maintenance and reliable monitoring.
Together, these benefits give Protix the operational confidence, while supporting sustainability goals and improving data-driven decision-making.
## Technologies Used
* **AWS Services:** AWS IoT Core, AWS Lambda, Amazon Timestream, Amazon Managed Grafana, AWS IoT Rules
* **Hardware:** Dragino LoRaWAN sensors and gateways
* **Protocol:** LoRaWAN
***
**Download the full case study:** [Protix AWS IoT Case Study (PDF)](/downloads/protix-aws-iot-case-study.pdf)
**Want similar results for your IoT project?** [Contact us](/en/about) to discuss your requirements.
### Tags
IoT AWS IoT Core Serverless AgriTech LoRaWAN
## Ready for Your Success Story?
Let's discuss how we can help you achieve similar results
[View All Case Studies ](/en/case-studies)
[ Get in Touch](mailto:info@forrict.nl)
---
# Cookie Policy
> This Cookie Policy explains how Forrict uses cookies and similar technologies on our website www.forrict.nl. By using our website, you agree to the use of
Last updated: January 2025
This Cookie Policy explains how Forrict uses cookies and similar technologies on our website www\.forrict.nl. By using our website, you agree to the use of cookies as described in this policy.
## What Are Cookies?
Cookies are small text files that are stored on your device when you visit a website. They help the website remember your preferences and improve your browsing experience.
## How We Use Cookies
We use cookies for the following purposes:
* **Essential cookies:** Required for the website to function properly
* **Analytics cookies:** To understand how visitors use our website
* **Marketing cookies:** To deliver relevant advertisements and track campaign performance
## Cookies We Use
| Cookie Name | Purpose | Type | Duration |
| ------------------------ | ------------------------------------------ | --------- | -------- |
| forrict\_cookie\_consent | Stores your cookie consent preferences | Necessary | 1 year |
| \_ga | Google Analytics - distinguishes users | Analytics | 2 years |
| \_ga\_\* | Google Analytics - stores session state | Analytics | 2 years |
| \_gid | Google Analytics - distinguishes users | Analytics | 24 hours |
| li\_fat\_id | LinkedIn Insight Tag - conversion tracking | Marketing | 30 days |
| \_gcl\_au | Google Ads - conversion tracking | Marketing | 3 months |
## Third-Party Cookies
We use the following third-party services that may set cookies:
### Google Analytics
To analyze website traffic and user behavior. For more information, see Google's Privacy Policy. [Learn more →](https://policies.google.com/privacy)
### Google Tag Manager
To manage and deploy marketing tags without modifying code. [Learn more →](https://policies.google.com/privacy)
### LinkedIn Insight Tag
To track conversions and target advertising. For more information, see LinkedIn's Cookie Policy. [Learn more →](https://www.linkedin.com/legal/cookie-policy)
## How to Manage Cookies
You can control cookies in several ways:
* **Cookie Banner:** Use our cookie banner to accept or reject non-essential cookies
* **Browser Settings:** Most browsers allow you to refuse or delete cookies. Instructions vary by browser
* **Opt-out Tools:** Use tools like [Google Analytics Opt-out Browser Add-on](https://tools.google.com/dlpage/gaoptout)
Note: Disabling necessary cookies may affect the functionality of our website.
## Google Consent Mode v2
We use Google Consent Mode v2 to respect your privacy choices. This means analytics and marketing cookies only load after you provide consent.
## Data Retention
* Analytics data is retained for 14 months
* Cookie consent preferences are stored for 1 year
* Marketing cookies expire after 30-90 days depending on the platform
## Changes to This Policy
We may update this Cookie Policy from time to time. The "Last updated" date at the top indicates when changes were last made.
## Contact Us
If you have questions about our use of cookies, contact us:
**Email:**
**Address:** Waspikseweg 25, 5109PE 's-Gravenmoer, Netherlands
---
# Open Clear Well-architected.
> Discover how Forrict helps businesses achieve success by leveraging AWS to drive innovation, efficiency, and growth through our proven methodology.
We don’t hide behind complex frameworks or endless consulting cycles. We keep things simple: Build what matters. Share everything we do. Leave you stronger than you started. That’s the Forrict way.
### Our Principles
Our principles aren’t posters on a wall they’re how we deliver real value, every day. And because we apply them from the very first conversation to the final handover, working with Forrict feels clear, collaborative, and refreshingly predictable. Here’s how that looks in practice.
1
### Radical clarity
No vague deliverables, no surprises. You always can see what we’re doing in real time and in real code.
2
### Open by default
Every line of code, every architectural choice, every diagram is shared. No lock-in. Ever.
3
### Quality over shortcuts
If it isn’t secure, scalable, and maintainable, we don’t ship it. This is AWS done properly.
4
### Empowerment built in
We aim to make your team independent. We’ll guide you as long as you need us not longer.
### The Forrict Way of Working
This approach keeps you in control while giving you access to deep AWS expertise and battle-tested craftsmanship. Whether you want us hands-on, hands-off, or somewhere in between, the goal is always the same: help your team move faster, safer, and smarter without creating dependency.
1
### Discovery, We get aligned.
We start with honest conversations: What are you trying to achieve? What’s slowing you down?
2
### Architect, We design the smart way forward.
We sketch a solution blueprint based on AWS Well-Architected principles. No buzzwords, no black boxes.
3
### Build, Quality first.
Code is delivered continuously, openly, and transparently. You see progress, you give feedback, you learn with us.
4
### Operate, We run your cloud with you.
If you want us to help or fully operate your AWS environment, we’re here. You stay in control. we bring reliability, monitoring, and ongoing improvements.
5
### Empower, We make ourselves less necessary.
You grow, your team grows, your cloud grows and we reduce friction instead of adding dependency.
## Ready to work the smart way?
Let’s build something secure, scalable, and future-proof together.
[ Start Your Journey ](mailto:info@forrict.nl)
[Read Our Blog](/en/blog)
---
# Stay in the loop
> Subscribe to get practical AWS tips, cloud cost insights, and security best practices delivered straight to your inbox. No spam, unsubscribe anytime.
Subscribe to get practical AWS tips, cloud cost insights, and security best practices delivered straight to your inbox. No spam, unsubscribe anytime.
### Stay in the loop
Get AWS insights and tips delivered to your inbox.
First name (optional)[Your email address]()Subscribe
---
# Privacy Policy
> Forrict ("we", "our", or "us") respects your privacy and is committed to protecting your personal data. This privacy policy explains how we collect, use, a
Last updated: January 2025
Forrict ("we", "our", or "us") respects your privacy and is committed to protecting your personal data. This privacy policy explains how we collect, use, and protect your information when you visit our website www\.forrict.nl.
## 1. Information We Collect
* **Information you provide:** When you contact us or fill out forms on our website, we may collect your name, email address, company name, and any other information you choose to provide.
* **Automatically collected information:** We collect technical information such as your IP address, browser type, device information, and how you interact with our website through cookies and similar technologies.
* **Analytics data:** With your consent, we use Google Analytics to understand how visitors use our website.
## 2. How We Use Your Information
* To respond to your inquiries and provide customer support
* To improve our website and services
* To analyze website usage and performance
* To send you marketing communications (with your consent)
* To comply with legal obligations
## 3. Legal Basis for Processing (GDPR)
* **Consent:** When you provide consent for marketing communications or analytics cookies
* **Legitimate interests:** For improving our services and website functionality
* **Contract performance:** When necessary to fulfill our services
* **Legal compliance:** When required by law
## 4. Data Sharing and Third Parties
* We do not sell your personal data. We may share your information with:
* **Service providers:** Google Analytics (analytics), Google Tag Manager (tag management), LinkedIn (marketing, with your consent)
* **Legal requirements:** When required by law or to protect our rights
## 5. Your Rights Under GDPR
* **Right to access:** Request a copy of your personal data
* **Right to rectification:** Correct inaccurate personal data
* **Right to erasure:** Request deletion of your personal data
* **Right to restrict processing:** Limit how we use your data
* **Right to data portability:** Receive your data in a structured format
* **Right to object:** Object to processing of your personal data
* **Right to withdraw consent:** Withdraw consent at any time
* To exercise these rights, contact us at info\@forrict.nl
## 6. Data Retention
* We retain your personal data only as long as necessary for the purposes outlined in this policy or as required by law. Analytics data is retained for 14 months.
## 7. Data Security
* We implement appropriate technical and organizational measures to protect your personal data against unauthorized access, alteration, disclosure, or destruction.
## 8. Cookies
* We use cookies and similar technologies. For detailed information about the cookies we use, please see our [Cookie Policy](/en/cookie-policy).
## 9. International Data Transfers
* Your data may be transferred to and processed in countries outside the European Economic Area (EEA). We ensure appropriate safeguards are in place, such as Standard Contractual Clauses.
## 10. Changes to This Policy
* We may update this privacy policy from time to time. The "Last updated" date at the top indicates when the policy was last revised.
## 11. Contact Us
* If you have questions about this privacy policy or wish to exercise your rights, contact us:
* **Email:** info\@forrict.nl
* **Address:** Waspikseweg 25, 5109PE 's-Gravenmoer, Netherlands
---
# Our Services
> Expert AWS consulting services tailored to your needs
1. [Home](/en/)
2. /
3. Services
Expert AWS consulting services tailored to your needs
### FinOps & Cost Optimization
Stay in control of your AWS costs, without slowing down.
Cloud Consulting finops
[Learn more ](/en/services/Finops)
### Flex consult
AWS expertise, exactly when you need it.
Cloud Consulting Flex-consulting
[Learn more ](/en/services/Flex-consult)
### Security assessment
Clear insight into your AWS security, without the stress.
Cloud Consulting Security Review
[Learn more ](/en/services/Security-assessment)
### Landingzones & Governance
Start secure. Scale without chaos.
Landingzone aws governance
[Learn more ](/en/services/landingzones)
### Managed AWS
We run your AWS, you stay in control.
managed aws aws managed services
[Learn more ](/en/services/managed-aws)
### Well architected review
A clear, practical review of your AWS environment.
Cloud Consulting Well Architect Review
[Learn more ](/en/services/well-architected-review)
## Ready to Transform Your AWS Infrastructure?
Let's discuss how we can help optimize your cloud journey
[ Contact Us ](mailto:info@forrict.nl)
[How We Work](/en/how-we-work)
---
# FinOps & Cost Optimization
> Stay in control of your AWS costs, without slowing down.
AWS makes scaling fast and easy — but costs can spiral just as quickly. Forrict helps teams understand, steer, and predict their cloud spend, so money becomes a tool again instead of a surprise.
## Why AWS costs often get out of control
It’s rarely caused by a single mistake. More often, it’s a combination of:
* Rapidly growing workloads
* Limited visibility per team or product
* No clear ownership of costs
* Optimization that happens too late, or not at all
The result: rising bills and growing uncertainty, while no one really knows where the money is going.
## FinOps, the Forrict way
For us, FinOps isn’t a tool, a dashboard, or a finance-only exercise. It’s a practical way of working together — across engineering, product, and finance.
We help you:
* Gain clear insight into where your money goes
* Link costs to teams and decisions
* Make informed choices about growth
* Reduce waste without adding risk
Always transparent. Always together.
## What this gives you
* Predictable AWS costs
* Less waste
* More confidence for finance and leadership
* Clear insights for engineering teams
* Room to keep innovating
In short: control without slowing growth.
### Ready to Get Started?
Let's discuss your AWS project and how we can help achieve your goals.
[Contact Us ](mailto:info@forrict.nl)
[How We Work](/en/how-we-work)
## Related Services
### [Flex consult](/en/services/Flex-consult)
[AWS expertise, exactly when you need it.](/en/services/Flex-consult)
[Learn more →](/en/services/Flex-consult)
### [Security assessment](/en/services/Security-assessment)
[Clear insight into your AWS security, without the stress.](/en/services/Security-assessment)
[Learn more →](/en/services/Security-assessment)
### [Landingzones & Governance](/en/services/landingzones)
[Start secure. Scale without chaos.](/en/services/landingzones)
[Learn more →](/en/services/landingzones)
## Ready to Transform Your AWS Infrastructure?
Let's discuss how we can help optimize your cloud journey
[Contact Us ](mailto:info@forrict.nl)
[View all services](/en/services)
---
# Flex consult
> AWS expertise, exactly when you need it.
Sometimes you don’t need a full project or managed service. You just need a clear answer, a second opinion, or hands-on help, fast. Flex Consult gives you direct access to experienced AWS experts, without contracts, commitments, or complexity.
## When Flex Consult is a good fit
Flex Consult works especially well if you:
* Have an AWS question you want answered now
* Need a quick architecture review
* Want a second opinion before making a decision
* Are dealing with a security or cost concern
* Need help unblocking your team
* Want expert input without handing everything over
Short feedback loops. Clear answers. No overhead.
## What we help with
Flex Consult can be used for things like:
* Architecture reviews and design decisions
* Security and compliance questions
* Cost and FinOps reviews
* AWS account and landing zone advice
* CI/CD and infrastructure setup
* Incident reviews and troubleshooting
* Scaling and performance questions
If it touches AWS, we can help.
## How it works
1. You book time when you need it,
2. We jump in remote, focused, and prepared
3. We work together, live
4. You leave with clarity, next steps, and full ownership
No reports you won’t read. No vague advice. Just practical help you can act on immediately.
## What you get
* Direct access to senior AWS expertise
* Clear, honest answers
* Practical guidance tailored to your setup
* Full transparency in everything we do
* Knowledge you can reuse inside your team
Need AWS help right now? Whether it’s one hour or a few sessions, Flex Consult adapts to your needs.
### Ready to Get Started?
Let's discuss your AWS project and how we can help achieve your goals.
[Contact Us ](mailto:info@forrict.nl)
[How We Work](/en/how-we-work)
## Related Services
### [FinOps & Cost Optimization](/en/services/Finops)
[Stay in control of your AWS costs, without slowing down.](/en/services/Finops)
[Learn more →](/en/services/Finops)
### [Security assessment](/en/services/Security-assessment)
[Clear insight into your AWS security, without the stress.](/en/services/Security-assessment)
[Learn more →](/en/services/Security-assessment)
### [Landingzones & Governance](/en/services/landingzones)
[Start secure. Scale without chaos.](/en/services/landingzones)
[Learn more →](/en/services/landingzones)
## Ready to Transform Your AWS Infrastructure?
Let's discuss how we can help optimize your cloud journey
[Contact Us ](mailto:info@forrict.nl)
[View all services](/en/services)
---
# Landingzones & Governance
> Start secure. Scale without chaos.
Your first architectural decisions on AWS have long-term impact. A well-designed landing zone gives your team a secure, scalable foundation, and prevents complexity from creeping in as you grow.
Forrict helps you build AWS foundations that are clear, predictable, and fully under your control.
## Why landing zones matter
Without a solid foundation, AWS environments tend to grow organically, and unpredictably. Accounts multiply, permissions drift, costs become harder to track, and security controls slowly weaken.
A strong landing zone helps you:
* scale safely across teams and environments
* reduce security and compliance risk
* keep costs visible and predictable
* avoid rework later on
It’s much easier to build this right from the start than to fix it later.
## What a Forrict landing zone includes
Every landing zone is tailored, but typically includes:
* A multi-account structure with clear separation
* Centralized identity and access management (IAM)
* Network design and segmentation
* Logging, monitoring, and audit trails
* Security baselines and guardrails
* Cost visibility and account structure
* Automation for account provisioning
* All built using AWS best practices and services.
## Governance without bureaucracy
Governance doesn’t have to slow teams down. At Forrict, governance means setting clear boundaries that help teams move faster and safer, not adding layers of approval.
We focus on:
* Guardrails instead of manual controls
* Automation over documentation
* Clear ownership and responsibilities
* Visibility instead of restriction
This way, teams know what’s allowed, what’s not, and why.
## How we build this with you
1. Understand your context Your teams, workloads, risks, and growth plans.
2. Design the foundation Clear architecture that fits your organization — not a generic template.
3. Build openly Everything is documented, explained, and visible.
4. Enable your team We make sure your team understands the setup and can work with it confidently.
No black boxes. No vendor lock-in.
## What you get
* A secure, scalable AWS foundation
* Clear account and permission structures
* Strong security and compliance baselines
* Easier operations and cost control
* A setup your team actually understands
You’re ready to grow, without losing control.
## When this is useful
Landing Zones & Governance are especially valuable if you:
* Are starting fresh on AWS
* Are growing beyond a single AWS account
* Need better security or compliance controls
* Want to standardize across teams
* Are tired of fixing foundational issues later
## Ready to build your AWS foundation?
Let’s design a landing zone that supports your growth, now and in the future.
### Ready to Get Started?
Let's discuss your AWS project and how we can help achieve your goals.
[Contact Us ](mailto:info@forrict.nl)
[How We Work](/en/how-we-work)
## Related Services
### [FinOps & Cost Optimization](/en/services/Finops)
[Stay in control of your AWS costs, without slowing down.](/en/services/Finops)
[Learn more →](/en/services/Finops)
### [Flex consult](/en/services/Flex-consult)
[AWS expertise, exactly when you need it.](/en/services/Flex-consult)
[Learn more →](/en/services/Flex-consult)
### [Security assessment](/en/services/Security-assessment)
[Clear insight into your AWS security, without the stress.](/en/services/Security-assessment)
[Learn more →](/en/services/Security-assessment)
## Ready to Transform Your AWS Infrastructure?
Let's discuss how we can help optimize your cloud journey
[Contact Us ](mailto:info@forrict.nl)
[View all services](/en/services)
---
# Managed AWS
> We run your AWS, you stay in control.
Running production workloads on AWS takes focus, discipline, and constant attention. Forrict helps teams keep their AWS environments stable, secure, and predictable — without turning operations into a black box.
You stay in the driver’s seat. We keep things running smoothly.
## When Managed AWS makes sense
Managed AWS is a good fit if:
* Your platform is growing and needs reliable operations
* Your team wants fewer operational distractions
* You need confidence around availability, security, and updates
* You don’t want to build a full ops team (yet)
* You still want visibility and control over your cloud
## How we operate AWS, differently
Managed AWS at Forrict is built on a few simple principles:
* Transparent by default, you see what we do and why
* Shared ownership, we work with your team, not around it
* No lock-in, everything is documented and accessible
* Predictable operations, no surprises, no hidden changes
We don’t “take over” your cloud. We help you run it better.
## What we handle
Depending on your setup, Managed AWS can include:
* Monitoring and alerting
* Incident response and troubleshooting
* Security updates and patching
* Backup and recovery processes
* AWS service updates and best practices
* Ongoing improvements to reliability and performance
All changes are discussed, documented, and visible.
## What you get
* A stable and reliable AWS environment
* Fewer incidents and less operational noise
* Clear insight into what’s running and why
* Confidence for your team and stakeholders
* More time to focus on building your product
Operations become predictable, not stressful.
## Who this is for
Managed AWS works best for teams that:
* Run production workloads on AWS
* Care about security and reliability
* Want operational support without losing control
* Prefer collaboration over outsourcing
## Ready for calmer AWS operations?
Let’s make your AWS environment reliable, predictable, and easy to work with.
### Ready to Get Started?
Let's discuss your AWS project and how we can help achieve your goals.
[Contact Us ](mailto:info@forrict.nl)
[How We Work](/en/how-we-work)
## Related Services
### [FinOps & Cost Optimization](/en/services/Finops)
[Stay in control of your AWS costs, without slowing down.](/en/services/Finops)
[Learn more →](/en/services/Finops)
### [Flex consult](/en/services/Flex-consult)
[AWS expertise, exactly when you need it.](/en/services/Flex-consult)
[Learn more →](/en/services/Flex-consult)
### [Security assessment](/en/services/Security-assessment)
[Clear insight into your AWS security, without the stress.](/en/services/Security-assessment)
[Learn more →](/en/services/Security-assessment)
## Ready to Transform Your AWS Infrastructure?
Let's discuss how we can help optimize your cloud journey
[Contact Us ](mailto:info@forrict.nl)
[View all services](/en/services)
---
# Security assessment
> Clear insight into your AWS security, without the stress.
Security shouldn’t feel vague, overwhelming, or purely compliance-driven. Forrict helps teams understand their AWS security posture, identify real risks, and improve step by step, without slowing development down.
## Why security assessments matter
As AWS environments grow, security risks often grow quietly along with them. Misconfigurations, missing controls, and unclear responsibilities can introduce risk without anyone noticing.
A focused security assessment helps you:
* understand where you stand today
* spot real risks early
* prioritize improvements
* build confidence with stakeholders
Not to point fingers, but to move forward safely.
## What we assess
Our security assessments focus on the areas that matter most in AWS, including:
* Identity and access management (IAM)
* Network security and segmentation
* Logging, monitoring, and detection
* Data protection and encryption
* Account and environment isolation
* Security guardrails and policies
* Always tailored to your setup and risk profile.
## How the assessment works
1. Scope & context We align on your environment, goals, and constraints.
2. Review & analysis We assess your AWS setup using AWS best practices and real-world experience.
3. Clear findings You get a focused overview of risks, gaps, and priorities, no noise.
4. Practical recommendations Actionable steps your team can actually implement.
This is a collaborative process, not an audit interrogation.
## What you get
* Clear insight into your current security posture
* A prioritized list of improvements
* Practical recommendations, not theory
* Shared understanding across teams
* A stronger, more resilient AWS environment
* Security becomes something you understand, not something you fear.
## When this is useful
A security assessment is especially valuable if:
* Your AWS environment has grown quickly
* You’re preparing for audits or certifications
* You want to reduce risk without slowing delivery
* You’re unsure if current controls are sufficient
* You want a second opinion from AWS experts
## Want clarity on your AWS security?
Let’s take a clear, calm look at your environment, and improve what really matters.
### Ready to Get Started?
Let's discuss your AWS project and how we can help achieve your goals.
[Contact Us ](mailto:info@forrict.nl)
[How We Work](/en/how-we-work)
## Related Services
### [FinOps & Cost Optimization](/en/services/Finops)
[Stay in control of your AWS costs, without slowing down.](/en/services/Finops)
[Learn more →](/en/services/Finops)
### [Flex consult](/en/services/Flex-consult)
[AWS expertise, exactly when you need it.](/en/services/Flex-consult)
[Learn more →](/en/services/Flex-consult)
### [Landingzones & Governance](/en/services/landingzones)
[Start secure. Scale without chaos.](/en/services/landingzones)
[Learn more →](/en/services/landingzones)
## Ready to Transform Your AWS Infrastructure?
Let's discuss how we can help optimize your cloud journey
[Contact Us ](mailto:info@forrict.nl)
[View all services](/en/services)
---
# Well architected review
> A clear, practical review of your AWS environment.
AWS gives you powerful building blocks, but over time, decisions add up. A Well-Architected Review helps you step back, look at the bigger picture, and improve your AWS setup where it matters most.
During the review, we will assess the workload on your AWS account thoroughly. Subsequently, you will receive a detailed report that highlights any high-risk findings uncovered during the assessment. Additionally, we will provide you with a custom improvement plan tailored to address and remedy the identified issues, ensuring your AWS environment is optimized to its fullest potential.
### Ready to Get Started?
Let's discuss your AWS project and how we can help achieve your goals.
[Contact Us ](mailto:info@forrict.nl)
[How We Work](/en/how-we-work)
## Related Services
### [FinOps & Cost Optimization](/en/services/Finops)
[Stay in control of your AWS costs, without slowing down.](/en/services/Finops)
[Learn more →](/en/services/Finops)
### [Flex consult](/en/services/Flex-consult)
[AWS expertise, exactly when you need it.](/en/services/Flex-consult)
[Learn more →](/en/services/Flex-consult)
### [Security assessment](/en/services/Security-assessment)
[Clear insight into your AWS security, without the stress.](/en/services/Security-assessment)
[Learn more →](/en/services/Security-assessment)
## Ready to Transform Your AWS Infrastructure?
Let's discuss how we can help optimize your cloud journey
[Contact Us ](mailto:info@forrict.nl)
[View all services](/en/services)
---
# Cloud zonder Gedoe
> 100% AWS-gefocust. We stemmen onze diensten af op jouw behoeften.
Forrict bouwt en beheert AWS-omgevingen met volledige transparantie en vakmanschap. Wij maken zowel je cloud als je team beter.
[Hoe we werken](/nl/how-we-work)[Neem contact op](mailto:info@forrict.nl)
## We werken met de volgende partners en tools





## Onze AWS Diensten
Cloud oplossingen op maat voor jouw bedrijf
### Well-Architected Review
Expert begeleiding over architectuur best practices door onze AWS Well-Architected review.
[Meer informatie](/nl/services/well-architected-review)
### Security Assessment
Versterk de security posture van je AWS Cloud met uitgebreide assessments.
[Meer informatie](/nl/services/Security-assessment)
### Flex Consult
Voldoe aan je cloud behoeften met flexibele on-demand consultancy en expert ondersteuning.
[Meer informatie](/nl/services/Flex-consult)
### FinOps
Maximaliseer je cloud voordeel met FinOps expertise, versnelt innovatie en optimaliseert uitgaven.
[Meer informatie](/nl/services/Finops)
### Managed AWS
24/7 beheer en monitoring van je AWS infrastructuur voor optimale prestaties.
[Meer informatie](/nl/services/managed-aws)
![AWS Select Tier Services Partner]()
Vertrouwde AWS Consulting Partner
## AWS Select Tier Partner
Forrict is een AWS Select Tier Services Partner, erkend voor onze expertise in het leveren van cloud oplossingen.
### What we excel at:
Cloud Architectuur
Security & Compliance
FinOps & Cost Optimalisatie
Managed Services
Migratie & Modernisatie
## Klaar voor de volgende stap in je cloud?
Wij helpen je jouw doelen te bereiken.
[Neem Contact Op](mailto:info@forrict.nl)
[Hoe We Werken ](/nl/how-we-work)
---
# Over Forrict
> Forrict is gespecialiseerd in AWS cloud architectuur en engineering. Onze hoogopgeleide professionals ontwerpen en implementeren veilige, schaalbare AWS oplossingen voor Nederlandse bedrijven.
## Ons verhaal
Forrict is ontstaan vanuit een simpel idee: cloud moet bedrijven sterker maken, niet afhankelijker.
We zagen te veel organisaties vastzitten in black-boxoplossingen, onduidelijke architecturen en leveranciers die alle kennis voor zichzelf hielden. Daarom hebben we een ander soort cloudpartner gecreëerd één die alles deelt, openlijk kennis overdraagt en ontwerpt met langdurige onafhankelijkheid als uitgangspunt.
## Onze Expertise
### Security & Compliance
AVG/GDPR compliance, security architectuur en implementatie van AWS security best practices.
### Cloud Architectuur
Well-Architected Framework implementatie, multi-account strategieën en schaalbare infrastructuur design.
### FinOps & Kostenoptimalisatie
Cloud kostenbeheer, resource optimalisatie en financiële governance voor AWS omgevingen.
### Migratie Services
Strategische cloud migratie planning en uitvoering met minimale downtime en risico.
### DevOps & Automatisering
CI/CD pipelines, infrastructure as code (CDK, CloudFormation) en automatiseringsoplossingen.
### Managed Services
24/7 AWS infrastructuur management, monitoring en ondersteuning voor bedrijfscontinuïteit.
## Waarom Kiezen voor Forrict?
### AWS Gecertificeerde Experts
Ons team heeft meerdere AWS certificeringen waaronder Solutions Architect Professional en Security Specialty
### Nederland Gericht
Diepgaand begrip van Nederlandse regelgeving, compliance vereisten en bedrijfscultuur
### Bewezen Track Record
Succesvol 25+ AWS projecten opgeleverd in financiële, gezondheidszorg en retail sectoren
### Kennisoverdracht
We implementeren niet alleen - we zorgen ervoor dat jouw team in staat is om AWS te beheren en optimaliseren
## Klaar om Samen te Werken?
Laten we bespreken hoe Forrict jouw AWS infrastructuur kan helpen transformeren
[ Neem Contact Op ](mailto:info@forrict.nl)
[Hoe We Werken](/nl/how-we-work)
---
# Getting Started with AWS CDK in TypeScript
> Start using AWS CDK with TypeScript, covering setup, deployment, and best practices

Start using AWS CDK with TypeScript, covering setup, deployment, and best practices
## Why CDK?
Infrastructure as Code (IaC) has changed how teams manage cloud infrastructure. AWS CDK builds on that idea by letting you define infrastructure using real programming languages instead of static templates.
Instead of writing large YAML or JSON files, you model infrastructure using TypeScript constructs, with type safety, refactoring support, and tests.
Learning CDK with TypeScript will transform your infrastructure workflows and enhance your engineering capabilities. With features like:
* Strong typing for catching errors early
* Robust testing capabilities
* Rich ecosystem support
## What is AWS CDK, and Why Should You Learn It?
### What is AWS CDK?
AWS CDK is an open-source framework that lets you define cloud infrastructure using code. Instead of writing verbose JSON or YAML templates, you can use TypeScript to manage resources like:
* S3 buckets
* Lambda functions
* VPCs
* And much more
```
// Example: Creating an S3 bucket with CDK
import * as cdk from 'aws-cdk-lib';
import * as s3 from 'aws-cdk-lib/aws-s3';
new s3.Bucket(this, 'MyBucket', {
versioned: true,
encryption: s3.BucketEncryption.S3_MANAGED,
});
```
### Key Benefits
1. **Simplified Infrastructure Management**
* No more manual setups
* Reduced human error
* Version control for your infrastructure
2. **Reusable Patterns**
* Create custom constructs
* Share across teams
* Maintain consistency
3. **Programming Features**
* Use loops and conditions
* Implement custom logic
* Leverage type safety
> 🚀 **Pro Tip**: Start with simple resources and gradually build up to more complex infrastructure patterns.
## Prerequisites for Getting Started
### Technical Requirements
Before diving in, ensure you have:
📋 **Essential Tools**
* AWS Account (free tier works fine)
* Node.js and npm (latest LTS version)
* AWS CLI configured
📋 **Development Environment**
* VS Code with TypeScrip extensions, or any other editor you like.
* Git for version control
* Terminal access
### Installation Steps
1. **Install Node.js**
```
# Check if Node.js is installed
node --version
# If not, download from nodejs.org
```
2. **Install AWS CDK CLI**
```
npm install -g aws-cdk
# Verify installation
cdk --version
```
3. **Configure AWS CLI**
```
aws configure
# Follow prompts for access key and secret
```
## Step-by-Step: Your First AWS CDK Project in TypeScript
### 1. Project Setup
Create your first CDK project:
```
# Create project directory
mkdir cdk-project
cd cdk-project
# Initialize CDK app
cdk init app --language=typescript
```
Your project structure should look like this:
```
cdk-project/
├── bin/
│ └── cdk-project.ts # Entry point
├── lib/
│ └── cdk-project-stack.ts # Stack definition
├── test/
│ └── cdk-project.test.ts # Tests
├── cdk.json
└── package.json
```
### 2. Creating Your First Stack
Open `lib/cdk-project-stack.ts` and add:
```
import * as cdk from 'aws-cdk-lib';
import { Construct } from 'constructs';
import * as s3 from 'aws-cdk-lib/aws-s3';
export class CdkProjectStack extends cdk.Stack {
constructor(scope: Construct, id: string, props?: cdk.StackProps) {
super(scope, id, props);
// Create an S3 bucket
const bucket = new s3.Bucket(this, 'MyFirstBucket', {
versioned: true,
encryption: s3.BucketEncryption.S3_MANAGED,
removalPolicy: cdk.RemovalPolicy.DESTROY, // For testing only
});
// Output the bucket name
new cdk.CfnOutput(this, 'BucketName', {
value: bucket.bucketName,
description: 'The name of the S3 bucket',
});
}
}
```
### 3. Deployment
Deploy your stack:
```
# Synthesize CloudFormation template
cdk synth
# Deploy to AWS
cdk deploy
```
> ⚠️ **Important**: Always review the changes before deploying:
>
> ```
> cdk diff
> ```
### 4. Testing and Iteration
Add a lifecycle policy to your bucket:
```
const bucket = new s3.Bucket(this, 'MyFirstBucket', {
versioned: true,
encryption: s3.BucketEncryption.S3_MANAGED,
removalPolicy: cdk.RemovalPolicy.DESTROY,
lifecycleRules: [
{
expiration: cdk.Duration.days(365),
transitions: [
{
storageClass: s3.StorageClass.INFREQUENT_ACCESS,
transitionAfter: cdk.Duration.days(30),
},
],
},
],
});
```
> 📚 **Further Reading**: Check out the [AWS CDK Workshop](https://cdkworkshop.com) for hands-on exercises.
F
### Fons Biemans
AWS expert en consultant bij Forrict, gespecialiseerd in cloud architectuur en AWS best practices voor Nederlandse bedrijven.
### Tags
AWS CDK TypeScript Infrastructure as Code Cloud Development
## Blijf op de hoogte
Ontvang AWS-inzichten en tips in je inbox.
### Blijf op de hoogte
Ontvang AWS-inzichten en tips in je inbox.
Voornaam (optioneel)[Jouw e-mailadres]()Aanmelden
## Gerelateerde Artikelen
[](/nl/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
14 apr 2026
### [AWS Landing Zones met CDK](/nl/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
Bouw veilige, schaalbare AWS landing zones met CDK. Leer over multi-account strategie, guardrails, account vending en waarom CDK de voorkeur verdient voor AWS-native infrastructuur.
[Lees meer](/nl/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
---
# AWS Landing Zones met CDK
> Bouw veilige, schaalbare AWS landing zones met CDK. Leer over multi-account strategie, guardrails, account vending en waarom CDK de voorkeur verdient voor AWS-native infrastructuur.

Bouw veilige, schaalbare AWS landing zones met CDK. Leer over multi-account strategie, guardrails, account vending en waarom CDK de voorkeur verdient voor AWS-native infrastructuur.
Je AWS-account is geen strategie. Tien onbeheerde accounts? Dat is een risico dat vanzelf bovenkomt bij je volgende audit.
We hebben dit uit ervaring geleerd. Toen we begonnen met het bouwen van landing zones voor bedrijven was het patroon altijd hetzelfde. Inconsistente security baselines. Developers die accounts aanmaken zonder enige guardrail. Een netwerkopzet bij elkaar gehouden door stamkennis en een Confluence-pagina die sinds 2021 niet meer is bijgewerkt.
Een landing zone lost dit op. Het is het fundament dat governance, security, kostenbeheersing en snelheid van ontwikkeling werkelijk laat samenwerken. Maar *hoe* je die landing zone bouwt, is minstens zo belangrijk als dat je er überhaupt een bouwt.
## Waarom enterprises een multi-account strategie nodig hebben
Je weet wat een AWS-account is. De vraag die er echt toe doet: waarom hebben organisaties met 5, 50 of 500 accounts een geformaliseerde aanpak nodig?
**Blast radius beperken.** Een verkeerd geconfigureerde IAM-rol in dev mag geen productiedata kunnen raken. Isolatie op account niveau is de sterkste grens die AWS biedt. Sterker dan VPCs, sterker dan IAM-policies. Gebruik het.
**Compliance op schaal.** AVG, SOC 2, NIS2. Het regelgevingslandschap blijft groeien. Handmatig elk account auditen is een verloren strijd. Je hebt guardrails nodig die overtredingen *voorkomen*, geen detective werk dat ze vindt als de schade al is aangericht.
**Kosten visibiliteit.** Zonder goede account structuur en afdwinging van tags vliegt je FinOps-team blind. We hebben organisaties gezien die zes cijfers aan niet-toe-te-wijzen kosten verbranden, simpelweg omdat niemand tagging vanaf dag één afdwong.
**Developer velocity.** Dit verrast mensen. Goede governance vertraagt teams niet. Wanneer een developer zelf een nieuw account kan aanvragen dat vooraf geconfigureerd komt met networking, logging en security baselines, shipt die sneller dan het team dat drie weken wacht tot IT alles handmatig heeft ingericht. We hebben dit bij klanten met eigen ogen gezien: goed ingerichte account vending maakte van een wekenlang proces een kwestie van minuten.
## De bouwstenen van een landing zone
Elke enterprise landing zone heeft deze componenten nodig, ongeacht welke tooling je kiest.
### 1. Account vending
Geautomatiseerde accountcreatie met vooraf geconfigureerde baselines. Een developer vraagt een workload-account aan en krijgt binnen minuten:
* Een account in de juiste OU met de juiste SCPs
* VPC met gestandaardiseerde CIDR-ranges, gekoppeld aan Transit Gateway of toegang tot een shared VPC
* CloudTrail, GuardDuty, Config en Security Hub ingeschakeld
* IAM Identity Center-toegang geconfigureerd
* Budget alerts ingesteld
Geen tickets. Geen wachten. Geen handmatige opzet waarbij iemand een stap vergeet.
We behandelen account vending als een intern product, niet als een eenmalig project. Het heeft versioning, testing en een backlog nodig. De teams die accounts afnemen zijn je gebruikers, en hun ervaring doet ertoe.
### 2. Guardrails: SCPs en Config Rules
Service Control Policies zijn je eerste verdedigingslinie. Ze definiëren wat *niet* kan, ongeacht IAM-permissies:
* Voorkomen dat CloudTrail of GuardDuty wordt uitgeschakeld
* Deployments beperken tot goedgekeurde regio’s (`eu-west-1`, `eu-central-1`, essentieel voor de AVG)
* Publieke S3 buckets en onversleutelde EBS volumes blokkeren
* Specifieke tags vereisen op alle resources
AWS Config rules vullen SCPs aan door continu drift te detecteren. Samen: preventieve *én* detectieve controles.
Ons advies? Begin streng. Zet alles op slot. Het is véél makkelijker om een guardrail te versoepelen voor een legitieme use case dan om er achteraf een af te dwingen nadat teams eromheen hebben gebouwd.
### 3. Networking
Transit Gateway als ruggengraat, die workload-VPCs verbindt met shared services en on-premises netwerken. De belangrijkste keuzes:
* Hub-and-spoke vs. Shared VPC’s
* Gecentraliseerde vs. gedistribueerde egress
* DNS-resolutiestrategie (Route 53 Resolver rules)
* Plaatsing van Network Firewall
Krijg je networking niet goed, dan heeft de rest daar last van. Dit is consequent waar we de meeste technical debt zien bij organisaties die hun AWS-footprint organisch hebben laten groeien.
### 4. Identity en access
IAM Identity Center voor menselijke toegang. Federeer met je bestaande IdP (Entra ID, Okta) en definieer permission sets die aansluiten bij je organisatierollen.
Voor machine-to-machine: IAM roles met duidelijk afgebakende policies. Cross-account toegang via role assumption. Nooit langlevende credentials. We verbazen ons er nog steeds over hoeveel enterprise-omgevingen we tegenkomen met statische access keys die ouder zijn dan sommige teamleden die ze gebruiken.
### 5. Gecentraliseerde logging en security
Een dedicated Log Archive-account dat verzamelt:
* CloudTrail organization trails
* VPC Flow Logs
* Config snapshots en compliance-historie
* GuardDuty- en Security Hub-bevindingen
Een apart Security Tooling-account draait je automatisering: remediation lambdas, SIEM-integraties, compliance dashboards. Houd security tooling gescheiden van de logs waar het op acteert.
## Wat de documentatie je niet vertelt
We hebben er genoeg gebouwd om te weten waar de echte valkuilen zitten. Dit hadden we graag eerder geweten.
**Test je landing zone als software.** We gebruiken CDK’s assertion testing om te valideren dat constructs de verwachte CloudFormation-output produceren. We testen SCPs tegen realistische scenario’s. We draaien `cdk-nag` in CI. Infrastructuurcode verdient dezelfde kwaliteitslat als applicatiecode. De meeste organisaties behandelen het niet zo, en dat betalen ze later.
**Negeer day-two operaties niet.** Een landing zone die prachtig deployt maar niet veilig ge-update kan worden, is een tikkende tijdbom. Ontwerp vanaf het begin voor incrementele updates. CDK’s `cdk diff` en gefaseerde rollouts maken dit beheersbaar, maar alleen als je er vooraf voor plant.
**FinOps vanaf dag één.** Bak cost allocation tags, budget alerts en anomaly detection in je baseline. Kostenvisibiliteit achteraf inbouwen na 18 maanden ongetagde resources is pijnlijk en duur. We hebben klanten geholpen hun AWS-rekening met 30% te verlagen, puur door goede tagging en accountstructuur in te richten. Dat is geen optimalisatie, dat is zichtbaarheid.
**Code-eigenaarschap is niet onderhandelbaar.** Dit zit in het DNA van hoe we bij Forrict werken. Elke regel CDK-code die we schrijven voor je landing zone? Die is van jou. De Git-repo, de pipeline, het deploymentproces, alles van jou. We creëren geen vendor lock-in naar onszelf. Als wij weggaan, moet je je landing zone zelfstandig kunnen onderhouden en doorontwikkelen. Dat is freedom through craftsmanship.
## Klaar om je AWS-fundament te bouwen?
Een degelijke landing zone is het verschil tussen een AWS-omgeving die met vertrouwen schaalt en een die kwetsbaarder wordt naarmate je groeit. De investering verdient zichzelf terug in security posture, compliance readiness, developer productivity en kostenvisibiliteit.
Bij Forrict bouwen we landing zones die volledig van jou zijn. Geen proprietary tools, geen managed-service lock-in. Solide CDK-code, beproefde patronen en de kennisoverdracht om het zelf te draaien.
**Wil je je AWS-fundament goed neerzetten?** [**Laten we praten.**](https://forrict.nl/nl/contact/)
F
### Forrict
AWS expert en consultant bij Forrict, gespecialiseerd in cloud architectuur en AWS best practices voor Nederlandse bedrijven.
### Tags
AWS CDK Landing Zones Multi-Account Cloud Governance Infrastructure as Code
## Gratis: AWS Kostenoptimalisatie Checklist
Ontvang onze 20-punten checklist om je AWS-kosten tot 30% te verlagen.
### Ontvang jouw gratis download
Vul je gegevens in om de downloadlink te ontvangen.
Voornaam (optioneel)[Jouw e-mailadres]()Stuur mij de download
## Gerelateerde Artikelen
[](/nl/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
21 apr 2026
### [FinOps op AWS](/nl/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
Je geeft waarschijnlijk 30% te veel uit aan AWS. Ontdek de FinOps-strategieën waarmee Nederlandse enterprises hun cloudkosten terugdringen, van zombie-opruiming tot Savings Plans-optimalisatie.
[Lees meer](/nl/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
[](/nl/blog/2026-04-28-aws-waf-bot-protection-real-world)
28 apr 2026
### [Hoe wij een botaanval stopten met AWS WAF](/nl/blog/2026-04-28-aws-waf-bot-protection-real-world)
De aanmeldpagina van een klant werd aangevallen door bots. Nepaccounts, vernietigde e-mailreputatie en Tor-verkeer maakten traditionele blokkering zinloos. Zo losten we het op met AWS WAF.
[Lees meer](/nl/blog/2026-04-28-aws-waf-bot-protection-real-world)
[](/nl/blog/2026-05-05-aws-well-architected-reviews-health-check)
5 mei 2026
### [AWS Well-Architected Reviews](/nl/blog/2026-05-05-aws-well-architected-reviews-health-check)
Je AWS-architectuur is afgedwaald, je weet alleen niet hoe ver. Een Well-Architected Review vindt de gaten voordat ze incidenten worden. Dit kun je verwachten.
[Lees meer](/nl/blog/2026-05-05-aws-well-architected-reviews-health-check)
---
# FinOps op AWS
> Je geeft waarschijnlijk 30% te veel uit aan AWS. Ontdek de FinOps-strategieën waarmee Nederlandse enterprises hun cloudkosten terugdringen, van zombie-opruiming tot Savings Plans-optimalisatie.

Je geeft waarschijnlijk 30% te veel uit aan AWS. Ontdek de FinOps-strategieën waarmee Nederlandse enterprises hun cloudkosten terugdringen, van zombie-opruiming tot Savings Plans-optimalisatie.
**Je geeft waarschijnlijk 30% te veel uit aan AWS. Zo helpen wij klanten dat op te lossen.**
We deden afgelopen kwartaal een kostenreview voor een Nederlandse startup. Ze gaven €150K per maand uit aan AWS. Binnen zes weken bespaarden we €4K per maand, en de meeste aanpassingen waren gênant eenvoudig.
Cloudverspilling komt niet door één verkeerde keuze. Het zijn duizend kleine beslissingen die zich opstapelen. Een engineer kiest m5.xxlarge omdat dat vorig project werkte. Een testomgeving draait door in het weekend. Een oude snapshot blijft hangen omdat niemand weet of die nog nodig is. Vermenigvuldig dat met vijftig teams, en je hebt een serieus budgetlek.
Volgens Flexera’s State of the Cloud Report verspillen enterprises zo’n 30% van hun clouduitgaven. Voor Nederlandse bedrijven die €200K-500K per maand aan AWS uitgeven, is dat serieus geld. En het meeste is te fixen zonder ook maar één regel applicatiecode aan te raken.
## Niemand is eigenaar van de rekening
AWS-pricing is oprecht complex. Meer dan 300 services, elk met eigen dimensies: per uur, per GB, per request, per miljoen API-calls. Maar complexiteit is niet de hoofdoorzaak van overspending. Gebrek aan eigenaarschap wel.
We zien bij vrijwel elke klant dezelfde drie patronen:
1. **Geen tagging-strategie.** Zonder consistente resource tags kun je kosten niet toewijzen aan teams of projecten. De AWS-factuur is gewoon één groot getal waar niemand zich verantwoordelijk voor voelt.
2. **Dev/test draait 24/7.** Die staging-cluster die ‘s nachts en in het weekend doorloopt? Die verbrandt 65% van z’n budget aan lege uren.
3. **Standaard instance-formaten.** Engineers kiezen wat vorige keer werkte. Niemand checkt of t3.medium de daadwerkelijke load prima aankan.
Dit zijn geen engineering fouten. Het zijn organisatorische blinde vlekken. En die vragen om organisatorische oplossingen.
## Quick wins: waar het laaghangend fruit hangt
Voordat we het over cultuurverandering hebben (blijf erbij, we houden het praktisch), eerst de aanpassingen die snel geld opleveren.
### Ruim de zombies op
Elk AWS-account heeft ze. Ontkoppelde EBS volumes. Idle Elastic IPs. Vergeten load balancers. Snapshots van instances die maanden geleden zijn verwijderd. AWS ruimt ze niet voor je op. Ze blijven gewoon doorrekenen.
Verlaten resources zijn zowel een beveiligingsrisico als een kostenpost en ze komen verrassend vaak voor, zelfs in goed beheerde omgevingen. We hebben een gratis script gemaakt waarmee je de meest voorkomende gevallen in enkele minuten opspoort. \[Download het hier →]
Een systematische zombie-opruiming bespaart doorgaans 5-15% van de totale AWS-uitgaven. Dat is het soort rendement waarbij je je afvraagt waarom je het niet eerder hebt gedaan.
### Right-size je compute
Gartner schat dat 40% van alle cloud instances minstens één maat te groot is voor de daadwerkelijke workload. AWS Compute Optimizer laat precies zien waar.
Maar right-sizing is meer dan alleen kleiner gaan. Soms heb je een compleet andere instance family nodig. CPU-intensieve workloads horen op c5 of c7g, niet op general purpose m5. Data-intensieve applicaties zijn beter af met r5. En Graviton-instances (m7g, c7g, r7g) leveren zo’n 20% betere prijs-prestatie over de hele linie. Zelfde workload, lagere rekening.
| Optimalisatie | Typische Besparing | Inspanning |
| ------------------------ | ----------------------------- | ------------------------------- |
| Zombie-opruiming | 5-15% van totale spend | Laag, geautomatiseerde audit |
| Instance right-sizing | 10-30% op compute | Middel, vereist utilizatie-data |
| Savings Plans (baseline) | 25-40% op committed workloads | Middel, commitment-analyse |
| Non-prod scheduling | Tot 65% op dev/test compute | Laag, Instance Scheduler setup |
### Commit waar het logisch is
Savings Plans en Reserved Instances besparen tot 72% ten opzichte van On-Demand. De vangst: je committeert je aan een gebruiksniveau voor 1-3 jaar. Dat schrikt mensen af.
Dat hoeft niet. De truc is conservatief committen. Kijk naar je usage floor, de baseline die je haalt zelfs op zondagnacht om 3 uur. Dek die af met Compute Savings Plans voor maximale flexibiliteit. Leg EC2 Instance Savings Plans er alleen bovenop voor workloads waarvan je zeker weet dat ze niet veranderen. Houd het variabele deel On-Demand of Spot.
We hebben enterprises gezien die jaarlijks zes cijfers laten liggen omdat ze bang waren om te committen. Wees niet een van hen.
### Schakel non-productie omgevingen uit buiten kantooruren
Deze is bijna te makkelijk. Die acceptatie-omgeving hoeft echt niet te draaien om 2 uur ‘s nachts op zondag. AWS Instance Scheduler laat je operationele vensters definiëren (maandag tot vrijdag, 07:00-19:00) en stopt en start automatisch EC2- en RDS-instances.
Voor een typische dev/test-setup zijn dat 65% minder draaiuren. Over meerdere omgevingen heen telt dat snel op.
## Structurele winst: de veranderingen die blijven
Quick wins voelen goed. Maar als dezelfde verspillingspatronen elk kwartaal terugkomen, heb je het probleem niet opgelost.
### Tags zijn alles
Tags zijn het fundament van cloud cost management. Zonder tags vlieg je blind. Je kunt letterlijk niet beantwoorden “welk team geeft wat uit aan welk project.”
Elke resource heeft minimaal nodig:
* **Environment** — production, staging, development
* **Team/Owner** — wie is verantwoordelijk
* **Project/Cost Center** — waar worden de kosten geboekt
* **Application** — bij welk systeem hoort het
Maak tagging niet optioneel. Gebruik AWS Organizations SCPs en Tag Policies om compliance af te dwingen bij deployment, of pas ver-erving toe vanuit je AWS Account. Stel Tagging-regels in de CDK- en Terraform-templates, zodat teams geen untagged resources kunnen deployen, zelfs als ze het proberen.
### Maak kosten zichtbaar voor de mensen die ze maken
Zodra tagging op orde is, gebruik je AWS Cost and Usage Reports (CUR) om dashboards op teamniveau te bouwen. Wanneer engineering-leads dagelijks de AWS-spend van hun team zien bijwerken, niet ergens verstopt in een maandelijkse financiële PDF, verandert het gedrag vanzelf.
Dit gaat niet over schuld. Het gaat over eigenaarschap. Teams die hun kosten zien, nemen betere architectuurbeslissingen.
### Het FinOps groeipad
De FinOps Foundation deelt dit op in drie fases, en het is een handig mentaal model:
* **Crawl:** Zichtbaarheid. Tagging, Cost Explorer-dashboards, een baseline van de uitgaven.
* **Walk:** Actieve optimalisatie. Savings Plans aangekocht, maandelijkse right-sizing reviews, geautomatiseerde scheduling. Kosten-KPI’s per team.
* **Run:** Kosten als engineering-metric. Teams wegen kosten mee bij elke architectuurbeslissing. Unit economics (kosten per transactie, kosten per klant) sturen de optimalisatie.
De meeste Nederlandse enterprises waar wij mee werken zitten tussen Crawl en Walk. Dat is prima. De grootste besparingen vinden precies in die transitie plaats.
## Nederland loopt voorop in cloudadoptie — en in cloudverspilling
Nederland loopt voorop in Europa qua cloudadoptie. CBS-data laat zien dat 65-70% van de Nederlandse bedrijven cloudservices gebruikt, tegenover een EU-gemiddelde van zo’n 45%. Meer cloudadoptie betekent meer uitgaven, en meer potentiële verspilling op schaal.
Daar komt het regelgevingslandschap bovenop. AVG, NIS2 voor kritieke infrastructuur, DORA voor financiële dienstverlening. Elke compliance-tool, audit log en security scan die in je AWS-omgeving draait, kost geld. Als je die kosten niet bewust beheert, lopen ze snel uit de hand.
En dan is er de soevereiniteitskwestie. Veel Nederlandse bedrijven vereisen hosting binnen de EU, doorgaans AWS eu-west-1 (Ierland) of eu-central-1 (Frankfurt). Cross-region datatransfer is niet gratis. Regionale prijzen variëren. Dit zijn echte kostendimensies die bewuste optimalisatie verdienen.
## Hoe wij FinOps aanpakken bij Forrict
Wij doen geen eenmalige kostenaudits. We hebben gezien wat er dan gebeurt: de besparing houdt een kwartaal stand, en dan glijdt alles terug naar de baseline omdat niemand meer oplet.
Onze aanpak is continue FinOps, ingebed in je AWS-operatie:
1. **Baseline-assessment.** We analyseren je huidige uitgaven, identificeren verspilling en bouwen een geprioriteerde roadmap. Geen PDF van 50 pagina’s die stof vangt, maar een gerankte actielijst met verwachte besparing per item.
2. **Eerst de quick wins.** Zombies, right-sizing, scheduling. Dit levert doorgaans 20-30% besparing op in de eerste maand en bouwt momentum voor het structurele werk.
3. **Structurele implementatie.** Tagging-strategie, cost allocation, Savings Plans-inkoop, geautomatiseerde handhaving. Allemaal ingebouwd in je Landing Zone zodat het standaard aanstaat.
4. **Continue optimalisatie.** Maandelijkse kostenreviews, anomalie-alerts, architectuuraanbevelingen. FinOps is geen project dat eindigt. Het is een praktijk die zich opstapelt.
Alles wat we bouwen, is van jou. De dashboards, de automatisering, de CDK, Terraform-modules. Het is jouw code, in jouw repository. We locken je niet in een kostenmanagementplatform. We bouwen de capability op binnen jouw organisatie.
## Wat de cijfers laten zien
Voor een middelgroot Nederlands bedrijf dat €200K-500K per maand aan AWS uitgeeft:
| Optimalisatiegebied | Maandelijkse Besparing |
| --------------------------------- | ----------------------- |
| Zombie-opruiming + scheduling | €20K-75K |
| Right-sizing + Graviton-migratie | €20K-100K |
| Savings Plans-optimalisatie | €50K-150K |
| **Gecombineerd jaarlijks effect** | **€300K-1,2M per jaar** |
Deze ranges komen overeen met wat AWS FinOps-practitioners consistent rapporteren bij middelgrote Europese enterprises. Jouw resultaten zullen variëren, maar de richting is altijd dezelfde.
## Klaar om te ontdekken waar je geld naartoe gaat?
Weet je niet waar je moet beginnen? Boek een gratis AWS Waste Scan van 30 minuten. Deel vooraf alleen-lezen toegang tot Cost Explorer en we komen voorbereid met je drie grootste besparingsmogelijkheden, geen verkooppraatje, gewoon concrete inzichten. [\[Boek je gratis Waste Scan →\]](https://forrict.nl/nl/contact/)
***
*Forrict is een AWS Select Tier Partner gevestigd in Nederland, gespecialiseerd in Landing Zones, managed AWS-operaties en FinOps. We helpen Nederlandse enterprises met het bouwen van schaalbare, veilige cloudomgevingen en houden de kosten onder controle.*
F
### Forrict
AWS expert en consultant bij Forrict, gespecialiseerd in cloud architectuur en AWS best practices voor Nederlandse bedrijven.
### Tags
FinOps AWS Cost Optimization Cloud Costs Savings Plans Dutch Enterprise
## Blijf op de hoogte
Ontvang AWS-inzichten en tips in je inbox.
### Blijf op de hoogte
Ontvang AWS-inzichten en tips in je inbox.
Voornaam (optioneel)[Jouw e-mailadres]()Aanmelden
## Gerelateerde Artikelen
[](/nl/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
14 apr 2026
### [AWS Landing Zones met CDK](/nl/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
Bouw veilige, schaalbare AWS landing zones met CDK. Leer over multi-account strategie, guardrails, account vending en waarom CDK de voorkeur verdient voor AWS-native infrastructuur.
[Lees meer](/nl/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
[](/nl/blog/2026-04-28-aws-waf-bot-protection-real-world)
28 apr 2026
### [Hoe wij een botaanval stopten met AWS WAF](/nl/blog/2026-04-28-aws-waf-bot-protection-real-world)
De aanmeldpagina van een klant werd aangevallen door bots. Nepaccounts, vernietigde e-mailreputatie en Tor-verkeer maakten traditionele blokkering zinloos. Zo losten we het op met AWS WAF.
[Lees meer](/nl/blog/2026-04-28-aws-waf-bot-protection-real-world)
[](/nl/blog/2026-05-05-aws-well-architected-reviews-health-check)
5 mei 2026
### [AWS Well-Architected Reviews](/nl/blog/2026-05-05-aws-well-architected-reviews-health-check)
Je AWS-architectuur is afgedwaald, je weet alleen niet hoe ver. Een Well-Architected Review vindt de gaten voordat ze incidenten worden. Dit kun je verwachten.
[Lees meer](/nl/blog/2026-05-05-aws-well-architected-reviews-health-check)
---
# Hoe wij een botaanval stopten met AWS WAF
> De aanmeldpagina van een klant werd aangevallen door bots. Nepaccounts, vernietigde e-mailreputatie en Tor-verkeer maakten traditionele blokkering zinloos. Zo losten we het op met AWS WAF.

De aanmeldpagina van een klant werd aangevallen door bots. Nepaccounts, vernietigde e-mailreputatie en Tor-verkeer maakten traditionele blokkering zinloos. Zo losten we het op met AWS WAF.
Een klant belde ons op een vrijdag. Hun aanmeldpagina werd bestookt door bots. Honderden nepaccounts per uur, elk aangemaakt met een echt e-mailadres van een bestaand persoon. Hun systeem verstuurde braaf welkomstmails naar iedereen.
Het gevolg? De e-mailreputatie van hun domein ging in vrije val. Binnen enkele dagen dreigde hun domein op een blacklist te belanden en hun AWS SES-toegang te worden opgeschort. Dat is geen theoretisch risico, SES schort je daadwerkelijk op als je bounce- en klachtenpercentages de drempel overschrijden.
Ze hadden het nu nodig!
## Het probleem met traditionele verdediging
De voor de hand liggende eerste stap is blokkeren op IP-adres. Verdachte bronnen identificeren, blokkeren, klaar. Simpel.
Behalve dat deze bots via het Tor-netwerk routeerden. Elk verzoek kwam van een ander exit-node. Blokkeer één IP, een ander neemt het binnen seconden over. Dat is een gevecht dat je niet wint met rate limiting en IP-blacklists alleen.
De bots waren niet bijzonder geavanceerd in wat ze deden,
* account aanmaken,
* e-mail triggeren,
* herhalen,
maar ze waren zeer effectief in het verbergen van hun herkomst. Traditionele IP-gebaseerde maatregelen waren nutteloos.
## Waarom dit gevaarlijker was dan het leek
Op het eerste gezicht klinken nepregistraties als een irritatie. Vervelend, zeker. Maar gevaarlijk?
Ja, dit is waarom:
**E-mailreputatie is fragiel.** Wanneer je domein honderden e-mails stuurt naar adressen waarvan de eigenaren zich nooit hebben aangemeld, markeren die mensen ze als spam. Mailproviders merken dat op. Je domeinreputatie daalt. Legitieme e-mails, orderbevestigingen, wachtwoordresets, facturen, belanden in spamfolders. Of worden compleet geblokkeerd.
**AWS SES heeft harde limieten.** Amazon monitort je bouncepercentage, klachtenpercentage en verzendpatronen. Overschrijd de grens en SES plaatst je account onder review. Ga nog verder en ze schorsen je verzendmogelijkheid volledig op. Voor een bedrijf dat afhankelijk is van transactionele e-mail is dat een storing.
**Het escaleert snel.** Botaanvallen nemen niet af. Ze versnellen. Elk uur niets doen betekent meer nepaccounts, meer bounced e-mails en meer reputatieschade om te herstellen. Herstel van een geblokkeerd domein duurt weken. Soms maanden.
## AWS WAF: het juiste gereedschap
We implementeerden AWS WAF voor hun applicatie. WAF zit aan de edge en inspecteert HTTP-verzoeken voordat ze je backend bereiken. Het is native AWS, integreert met CloudFront, ALB en API Gateway, en geeft je fijnmazige controle over welk verkeer doorkomt.
Voor deze opdracht richtten we ons op drie dingen:
**Managed rule groups.** AWS WAF wordt geleverd met samengestelde regelsets die worden onderhouden door AWS en gecontroleerde derde partijen. Deze bevatten regels die specifiek zijn ontworpen om bekende kwaadwillende actoren te identificeren en te blokkeren, inclusief verkeer afkomstig van anonimiseringsnetwerken. We activeerden de relevante managed rules en filterden direct het meest voor de hand liggende botverkeer.
**Gedragspatroonherkenning.** Naast bekende verdachte IP-adressen configureerden we regels om de patronen te detecteren die deze bots vertoonden. De aanmeldverzoeken hadden kenmerken die ze onderscheidden van legitiem gebruikersgedrag. WAF stelde ons in staat regels te definiëren die deze patronen matchten zonder echte gebruikers te blokkeren.
**Rate-based rules.** Zelfs via Tor overschreed het volume van verzoeken vanaf individuele exit-nodes wat een legitieme gebruiker zou genereren. Rate-based rules voegden een extra laag toe en blokkeerden automatisch bronnen die redelijke drempels overschreden binnen een bepaald tijdsvenster.
De combinatie werkte. Binnen enkele uren daalden nepregistraties naar vrijwel nul.
## Het resultaat
| Metric | Voor | Na |
| -------------------------- | ------------------- | ------------------------------ |
| Nepregistraties per uur | Honderden | Vrijwel nul |
| SES bouncepercentage | Gevaarlijk hoog | Binnen veilige drempels |
| E-mailreputatie | Snel verslechterend | Gestabiliseerd en herstellende |
| Impact op echte gebruikers | Geen | Geen |
De e-mailstroom van de klant was hersteld. SES bleef actief. Echte gebruikers merkten niets.
## Verder dan de directe fix
De aanval stoppen was stap één. Maar botaanvallen komen niet één keer. Ze komen terug. Vaak slimmer.
AWS WAF is geen set-and-forget tool. Het vereist monitoring en bijsturing. We configureerden logging via WAF’s integratie met CloudWatch om geblokkeerde verzoeken te volgen, nieuwe patronen te identificeren en regels aan te passen naarmate het gedrag van aanvallers evolueert.
Voor bredere beveiligingsvisibiliteit adviseerden we de klant ook om GuardDuty en Security Hub in hun monitoringstack te integreren. GuardDuty detecteert ongewone activiteit op infrastructuurniveau, gecompromitteerde instances, afwijkende API-aanroepen, verkenningspatronen. Security Hub aggregeert bevindingen van WAF, GuardDuty en andere bronnen in één compliance-bewust dashboard.
Samen creëren deze drie diensten een gelaagde verdediging:
| Laag | Service | Wat het dekt |
| --------------------- | ------------ | ------------------------------------------------ |
| **Edge-bescherming** | AWS WAF | HTTP-filtering, botmitigatie, rate limiting |
| **Dreigingsdetectie** | GuardDuty | Infrastructuurdreigingen, afwijkend gedrag |
| **Postuurbeheer** | Security Hub | Geaggregeerde bevindingen, compliance-dashboards |
Geen enkele tool dekt alles. Maar correct gestapeld dekken ze elkaars blinde vlekken.
## De NIS2-invalshoek
Als je opereert in de EU, is botmitigatie niet alleen verstandig. Het wordt een compliance-vereiste.
NIS2, de bijgewerkte EU-richtlijn voor netwerk- en informatiebeveiliging, schrijft voor dat organisaties in essentiële en belangrijke sectoren passende maatregelen implementeren tegen cyberdreigingen. Botaanvallen die e-mailinfrastructuur compromitteren, frauduleuze accounts creëren of de beschikbaarheid van diensten verstoren, vallen volledig binnen dat bereik.
Een gedocumenteerde, geautomatiseerde responscapabiliteit (zoals WAF met managed rules en monitoring) demonstreert het soort “passende technische maatregelen” dat NIS2 verwacht. Het is niet het volledige complianceplaatje, maar het is een wezenlijk onderdeel.
## Als het misgaat, telt snelheid
Deze opdracht bevestigde iets dat we keer op keer zien: het verschil tussen een klein incident en een serieus incident is reactietijd.
De e-mailreputatie van de klant was al beschadigd toen ze ons belden. Nog een week niets doen en ze hadden te maken gehad met een geblokkeerd domein en opgeschorte SES-toegang, met cascaderende effecten op hun gehele zakelijke communicatie.
We hadden WAF geïmplementeerd en verkeer gefilterd binnen enkele uren. Niet omdat de technologie magisch is, maar omdat we dit vaker hebben gedaan. We wisten welke regels we moesten activeren, hoe we ze moesten configureren zonder legitieme gebruikers te blokkeren, en hoe we de resultaten moesten valideren onder druk.
Dat is wat je krijgt van een team dat elke dag in AWS leeft.
## Wacht niet op de aanval
De meeste organisaties denken pas aan botbescherming als de bots er al zijn. Tegen die tijd loopt de schade al op. WAF-regels die een uur kosten om te configureren tijdens normale operaties, kosten hetzelfde uur tijdens een incident, maar met veel meer stress en veel minder ruimte voor fouten.
Als je aanmeldformulieren, betaalpagina’s of andere publiek toegankelijke applicaties draait op AWS, is de vraag niet óf bots het vinden. Het is wanneer.
**Wij helpen je snel te reageren op dreigingen en de volgende te voorkomen.**
[Neem contact op over het beveiligen van je AWS-omgeving →](https://forrict.nl/nl/contact/)
F
### Forrict
AWS expert en consultant bij Forrict, gespecialiseerd in cloud architectuur en AWS best practices voor Nederlandse bedrijven.
### Tags
AWS WAF Bot Protection Cloud Security NIS2
## Blijf op de hoogte
Ontvang AWS-inzichten en tips in je inbox.
### Blijf op de hoogte
Ontvang AWS-inzichten en tips in je inbox.
Voornaam (optioneel)[Jouw e-mailadres]()Aanmelden
## Gerelateerde Artikelen
[](/nl/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
14 apr 2026
### [AWS Landing Zones met CDK](/nl/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
Bouw veilige, schaalbare AWS landing zones met CDK. Leer over multi-account strategie, guardrails, account vending en waarom CDK de voorkeur verdient voor AWS-native infrastructuur.
[Lees meer](/nl/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
[](/nl/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
21 apr 2026
### [FinOps op AWS](/nl/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
Je geeft waarschijnlijk 30% te veel uit aan AWS. Ontdek de FinOps-strategieën waarmee Nederlandse enterprises hun cloudkosten terugdringen, van zombie-opruiming tot Savings Plans-optimalisatie.
[Lees meer](/nl/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
[](/nl/blog/2026-05-05-aws-well-architected-reviews-health-check)
5 mei 2026
### [AWS Well-Architected Reviews](/nl/blog/2026-05-05-aws-well-architected-reviews-health-check)
Je AWS-architectuur is afgedwaald, je weet alleen niet hoe ver. Een Well-Architected Review vindt de gaten voordat ze incidenten worden. Dit kun je verwachten.
[Lees meer](/nl/blog/2026-05-05-aws-well-architected-reviews-health-check)
---
# AWS Well-Architected Reviews
> Je AWS-architectuur is afgedwaald, je weet alleen niet hoe ver. Een Well-Architected Review vindt de gaten voordat ze incidenten worden. Dit kun je verwachten.

Je AWS-architectuur is afgedwaald, je weet alleen niet hoe ver. Een Well-Architected Review vindt de gaten voordat ze incidenten worden. Dit kun je verwachten.
Je bent twee jaar geleden live gegaan op AWS. De architectuur was degelijk. Security was op orde, de kosten waren redelijk en het team kende elk onderdeel.
Spoel door naar vandaag. Drie teams deployen onafhankelijk van elkaar. Iemand heeft “tijdelijk” oversized instances opgestart, zes maanden geleden. Je disaster recovery plan staat op een Confluence-pagina die niemand heeft geopend sinds de initiële build. En die S3 bucket? Public read access sinds een demo in Q2.
Niemand bouwt bewust een puinhoop. Het sluipt erin.
## Wat het Well-Architected Framework eigenlijk is
Wij voeren regelmatig Well-Architected Reviews uit voor Nederlandse bedrijven, en wat de meeste teams verrast: het framework is geen theoretische checklist. Het is een gestructureerde set lastige vragen, ontworpen om precies die dingen boven water te halen waar je te druk voor was om naar te kijken.
AWS heeft het georganiseerd rond zes pijlers. Je hebt de lijst waarschijnlijk al eens gezien. Maar pijlers opsommen is makkelijk. De waarde zit in de vragen die elke pijler je dwingt eerlijk te beantwoorden.
**Operational Excellence** — Kan je team reageren op incidenten zonder heldendaden? Zijn deployments geautomatiseerd en herhaalbaar, of SSH’t er iemand om 2 uur ‘s nachts naar een server? Leer je van failures, of fix je het en ga je door?
**Security** — Wie heeft toegang tot wat, en hoe weet je dat? Is data encrypted at rest en in transit? Zou je een breach nu kunnen detecteren, niet morgen, niet nadat iemand iets vreemds opmerkt in CloudWatch?
**Reliability** — Wat gebeurt er als een component uitvalt? Heb je failover echt getest, of hoop je dat het runbook uit 2024 nog klopt? Kun je schalen zonder handmatige interventie?
**Performance Efficiency** — Gebruik je de juiste resource types? Wanneer heeft iemand voor het laatst gekeken of die instance families nog logisch zijn? Draai je containers op oversized EC2 terwijl Fargate de helft zou kosten?
**Cost Optimization** — Weet je wat elk team uitgeeft, en waarom? Betaal je voor resources die niemand gebruikt? Is je tagging strategy echt, of een spreadsheet die iemand ooit heeft ingevuld?
**Sustainability** — Minimaliseer je verspilde compute? Kun je dezelfde workload draaien op minder resources met slimmere architectuurkeuzes?
Elke pijler bevat tientallen specifieke vragen. Ze zijn ontworpen om blinde vlekken te vinden, de aannames die je team maakt omdat niemand ze recentelijk heeft gecontroleerd.
## Waarom architecturen afdwalen
Niemand wordt wakker en besluit een fragiele, dure, onveilige omgeving te bouwen. Drift is stiller dan dat.
Een feature wordt opgeleverd onder tijdsdruk. Het team slaat de architecture review over omdat “het maar een kleine wijziging is.” Vermenigvuldig dat met vijftig deployments over drie squads in achttien maanden. Nu ziet je omgeving er heel anders uit dan het oorspronkelijke ontwerp, en niemand kan aanwijzen wanneer het misging.
Dit zien we het vaakst:
| Bevinding | Wat er in de praktijk gebeurt |
| ------------------------------ | -------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Geen DR-testing** | Het disaster recovery plan bestaat. Het is geschreven tijdens de initiële build. Het is nooit uitgevoerd. Als het moment komt, weet niemand of het werkt. Hoop is geen recovery-strategie. |
| **Handmatige deployments** | Eén team heeft geautomatiseerd. Twee anderen deployen nog met de hand. Het is een kwestie van tijd voordat een handmatige push iets spannends introduceert in productie. |
| **Over-provisioned resources** | Die `m5.4xlarge` was gedimensioneerd voor piekbelasting die één keer voorkwam. Hij draait dagelijks op 12% CPU. Niemand heeft hem verkleind omdat “hij werkt.” Klopt, en hij verbrandt ondertussen geld. |
| **Ontbrekende encryptie** | Data at rest is encrypted in productie maar niet in staging. Staging bevat productiedata. Je ziet het probleem. |
| **Geen kostenallocatie** | De AWS-factuur komt binnen. Hij is hoger dan vorige maand. Niemand kan met vertrouwen uitleggen waarom. |
Dit zijn geen uitzonderingen. Dit zijn de meest voorkomende bevindingen bij de enterprises die wij reviewen.
## Hoe wij een Well-Architected Review uitvoeren
Een review is geen afvinkexercitie. Het is een gestructureerde deep dive in je workloads tegen de zes pijlers. Geen PDF van 200 pagina’s die stof verzamelt. Concrete bevindingen waar je maandagochtend mee aan de slag kunt.
### Discovery
We beginnen met het begrijpen van je landschap. Welke workloads draaien er? Wat is bedrijfskritisch? Wie deployt wat, en hoe? Hoe ziet je teamstructuur eruit?
Dit gaat niet over het auditen van je team. Het gaat over het begrijpen van context, zodat de bevindingen landen als uitvoerbare aanbevelingen, niet als abstract advies.
### Workload analyse
We beoordelen je architectuur tegen het framework met de AWS Well-Architected Tool en Trusted Advisor. Maar de tooling is slechts het startpunt. De echte waarde zit in engineers die met je team zitten, CDK- en Terraform-configuraties reviewen, deployment pipelines, monitoring, IAM policies, networking en kostenstructuur doorlopen. De vragen stellen die elke pijler vereist. Doorvragen op de antwoorden.
Dit is geen vulnerability scan. Het is geen geautomatiseerd rapport. Het is een gesprek.
### Bevindingen rapport
Je krijgt een helder, geprioriteerd rapport. Kritieke risico’s gescheiden van middellange-termijnverbeteringen, gescheiden van nice-to-haves.
Elke bevinding beschrijft wat het probleem is, waarom het ertoe doet, en wat je eraan kunt doen. Geen vaagheid. Geen consultantjargon. Als wij een bevinding niet in heldere taal kunnen uitleggen, hebben we hem zelf niet goed genoeg begrepen.
### Remediatie roadmap
Bevindingen zonder plan zijn alleen maar stress. We leveren een geprioriteerde roadmap: wat eerst te fixen, geschatte inspanning, en de verwachte impact van elke verandering.
Security gaps en single points of failure gaan naar de top. Kostenoptimalisatie wordt geordend op besparingspotentieel versus implementatie-inspanning. Je loopt weg met precies de kennis waar je moet beginnen en wat je voorlopig kunt negeren.
## Wat het je concreet oplevert
**Minder risico.** Je vindt de single points of failure, de onversleutelde datastores, de IAM policies met `*:*` die iemand drie jaar geleden “tijdelijk” heeft toegevoegd. De kosten van preventie zijn een fractie van de kosten van een breach of outage. Elke CTO weet dit intellectueel. Een review maakt het concreet.
**Lagere AWS-kosten.** Over-provisioned instances, ongebruikte Elastic IPs, vergeten snapshots, verkeerde pricing models. Het telt sneller op dan de meeste teams beseffen. Wij zien doorgaans 10-30% besparing op compute-uitgaven in de eerste optimalisatieronde. Sommige teams staren naar de cijfers en vragen zich af waarom ze zo lang hebben gewacht.
**Sterkere compliancepositie.** NIS2 is nu afdwingbaar in Nederland. GDPR-audits worden elke cyclus gedetailleerder. Nederlandse enterprises staan onder echte regelgevingsdruk om security controls aan te tonen, en het venster om je zaakjes op orde te krijgen sluit. Een Well-Architected Review mapt direct op deze frameworks. Het geeft je gedocumenteerd bewijs van je posture, of laat je precies zien waar de gaten zitten voordat een toezichthouder dat doet.
**Snellere incidentrespons.** Als je je architectuur door en door kent (wat faalt, wat herstelt, wat handmatige interventie nodig heeft), reageert je team sneller. Runbooks zijn gebaseerd op de werkelijkheid, niet op aannames uit de initiële build.
**Vertrouwen om te schalen.** Je kunt niet schalen wat je niet begrijpt. Een review geeft engineering leadership een helder beeld van waar de architectuur staat en wat er moet gebeuren voor de volgende groeifase.
## Wanneer moet je er een doen?
Er is geen verkeerd moment. Maar sommige momenten maken het extra waardevol:
* **Voor een grote migratie of uitbreiding.** Ken je baseline voordat je erop gaat bouwen.
* **Na snelle groei.** Als je team is verdubbeld of je workload verdrievoudigd, heeft je architectuur vrijwel zeker geen gelijke tred gehouden.
* **Jaarlijks, als hygiëne.** AWS brengt constant nieuwe services uit. Wat twee jaar geleden well-architected was, is dat vandaag misschien niet meer.
* **Na een incident.** Er is iets kapotgegaan. Een review helpt je de andere dingen te vinden die staan te wachten om kapot te gaan.
* **Voorafgaand aan compliance-deadlines.** NIS2 is van kracht. Een Well-Architected Review geeft je een voorsprong in het aantonen van je controls.
## Je architectuur is afgedwaald
Je AWS-omgeving staat niet stil. Je business verandert, je team verandert, AWS zelf verandert. Wat achttien maanden geleden goed was gebouwd, is afgedwaald. De enige vraag is hoe ver.
Een Well-Architected Review geeft je duidelijkheid. Geen verkooppraatje. Geen theoretisch framework. Een concrete beoordeling van waar je staat en wat je vervolgens moet doen.
[Plan een Well-Architected Review met Forrict](https://forrict.nl/nl/contact/) en ontdek waar je AWS-omgeving werkelijk staat.
F
### Forrict
AWS expert en consultant bij Forrict, gespecialiseerd in cloud architectuur en AWS best practices voor Nederlandse bedrijven.
### Tags
AWS Well-Architected Architecture Review Cloud Architecture NIS2 Cost Optimization
## Blijf op de hoogte
Ontvang AWS-inzichten en tips in je inbox.
### Blijf op de hoogte
Ontvang AWS-inzichten en tips in je inbox.
Voornaam (optioneel)[Jouw e-mailadres]()Aanmelden
## Gerelateerde Artikelen
[](/nl/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
14 apr 2026
### [AWS Landing Zones met CDK](/nl/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
Bouw veilige, schaalbare AWS landing zones met CDK. Leer over multi-account strategie, guardrails, account vending en waarom CDK de voorkeur verdient voor AWS-native infrastructuur.
[Lees meer](/nl/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
[](/nl/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
21 apr 2026
### [FinOps op AWS](/nl/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
Je geeft waarschijnlijk 30% te veel uit aan AWS. Ontdek de FinOps-strategieën waarmee Nederlandse enterprises hun cloudkosten terugdringen, van zombie-opruiming tot Savings Plans-optimalisatie.
[Lees meer](/nl/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
[](/nl/blog/2026-04-28-aws-waf-bot-protection-real-world)
28 apr 2026
### [Hoe wij een botaanval stopten met AWS WAF](/nl/blog/2026-04-28-aws-waf-bot-protection-real-world)
De aanmeldpagina van een klant werd aangevallen door bots. Nepaccounts, vernietigde e-mailreputatie en Tor-verkeer maakten traditionele blokkering zinloos. Zo losten we het op met AWS WAF.
[Lees meer](/nl/blog/2026-04-28-aws-waf-bot-protection-real-world)
---
# AWS Inzichten & Best Practices
> Expert inzichten over AWS cloud oplossingen, best practices en implementatiehandleidingen voor Nederlandse bedrijven
Expert begeleiding voor AWS cloud oplossingen, architectuurpatronen en implementatiestrategieën voor Nederlandse bedrijven
[](/nl/blog/2026-05-05-aws-well-architected-reviews-health-check)
5 mei 2026 Cloud Architecture
## [AWS Well-Architected Reviews](/nl/blog/2026-05-05-aws-well-architected-reviews-health-check)
Je AWS-architectuur is afgedwaald, je weet alleen niet hoe ver. Een Well-Architected Review vindt de gaten voordat ze incidenten worden. Dit kun je verwachten.
\#AWS Well-Architected #Architecture Review #Cloud Architecture
[Lees artikel ](/nl/blog/2026-05-05-aws-well-architected-reviews-health-check)
[](/nl/blog/2026-04-28-aws-waf-bot-protection-real-world)
28 april 2026 Security
## [Hoe wij een botaanval stopten met AWS WAF](/nl/blog/2026-04-28-aws-waf-bot-protection-real-world)
De aanmeldpagina van een klant werd aangevallen door bots. Nepaccounts, vernietigde e-mailreputatie en Tor-verkeer maakten traditionele blokkering zinloos. Zo losten we het op met AWS WAF.
\#AWS WAF #Bot Protection #Cloud Security
[Lees artikel ](/nl/blog/2026-04-28-aws-waf-bot-protection-real-world)
[](/nl/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
21 april 2026 FinOps
## [FinOps op AWS](/nl/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
Je geeft waarschijnlijk 30% te veel uit aan AWS. Ontdek de FinOps-strategieën waarmee Nederlandse enterprises hun cloudkosten terugdringen, van zombie-opruiming tot Savings Plans-optimalisatie.
\#FinOps #AWS Cost Optimization #Cloud Costs
[Lees artikel ](/nl/blog/2026-04-21-finops-aws-dutch-enterprises-cut-cloud-costs)
[](/nl/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
14 april 2026 Cloud Infrastructure
## [AWS Landing Zones met CDK](/nl/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
Bouw veilige, schaalbare AWS landing zones met CDK. Leer over multi-account strategie, guardrails, account vending en waarom CDK de voorkeur verdient voor AWS-native infrastructuur.
\#AWS CDK #Landing Zones #Multi-Account
[Lees artikel ](/nl/blog/2026-04-14-aws-landing-zones-cdk-practical-guide)
[](/nl/blog/2025-12-22-getting-started-aws-cdk-typescript)
22 december 2025 Cloud Infrastructure
## [Getting Started with AWS CDK in TypeScript](/nl/blog/2025-12-22-getting-started-aws-cdk-typescript)
Start using AWS CDK with TypeScript, covering setup, deployment, and best practices
\#AWS CDK #TypeScript #Infrastructure as Code
[Lees artikel ](/nl/blog/2025-12-22-getting-started-aws-cdk-typescript)
Weergave 5 van 5 artikelen
---
# Succesverhalen
> Ontdek hoe we andere hebben geholpen hun AWS infrastructuur te transformeren met echte succesverhalen en meetbare resultaten.
1. [Home](/nl/)
2. /
3. Succesverhalen
Echte resultaten van andere. Zie hoe we bedrijven hebben geholpen hun AWS infrastructuur te transformeren.
25+
Opgeleverde Projecten
40%
Gem. Kostenreductie
24/7
Support Beschikbaar
 AgriTech / IoT
Protix
### [Protix Gebruikt AWS IoT voor Schaalbare Insectenproductie Monitoring](/nl/case-studies/protix-aws-iot)
Hoe Forrict een serverless AWS IoT-oplossing implementeerde om het vendor-locked monitoringsysteem van Protix te vervangen, waardoor de sensor uptime steeg van 1 maand naar 5-7 jaar.
Sensor uptime verhoogd van 1 maand naar 5-7 jaar
Sensor onboarding teruggebracht naar 15 minuten
50% lagere meetkosten
IoT AWS IoT Core Serverless
[Lees volledig verhaal ](/nl/case-studies/protix-aws-iot)
## Klaar om Jouw Succesverhaal te Schrijven?
Laten we bespreken hoe we jouw AWS infrastructuur kunnen transformeren
[ Neem Contact Op ](mailto:info@forrict.nl)
[Hoe We Werken](/nl/how-we-work)
---
# Protix Gebruikt AWS IoT voor Schaalbare Insectenproductie Monitoring
> Hoe Forrict een serverless AWS IoT-oplossing implementeerde om het vendor-locked monitoringsysteem van Protix te vervangen, waardoor de sensor uptime steeg van 1 maand naar 5-7 jaar.
## Belangrijkste Resultaten
Sensor uptime verhoogd van 1 maand naar 5-7 jaar
Sensor onboarding teruggebracht naar 15 minuten
50% lagere meetkosten
1 jaar historische data retentie
Vendor lock-in geëlimineerd

## Over de Klant
Protix is een Nederlands agritech bedrijf met hoofdkantoor in Den Bosch en een unieke insectenfabriek in Bergen op Zoom. Als pionier in insect-gebaseerde voeding kweekt Protix black soldier vlieg larven om duurzame proteïne en lipiden te produceren van plantaardige bijproducten. Deze ingrediënten vervangen traditionele diervoedercomponenten zoals vismeel, wat bijdraagt aan circulaire landbouw en het verminderen van milieu-impact.
## De Uitdaging
Protix vertrouwde op IoT-gebaseerde sensoren om temperatuur- en vochtigheidsomstandigheden in hun R\&D-faciliteiten te monitoren. Deze sensoren werkten in een gesloten, vendor-locked systeem met een beperkte set ondersteunde apparaten, waardoor het moeilijk was om:
* **Sensordekking uit te breiden** over faciliteiten
* **Nieuwe sensortypes te integreren** voor verschillende metingen
* **Data te benaderen** voor geavanceerde analyses
De hardware ging met regelmatig defect wat kostbaar onderhoud vereiste. Defecten moest vaak vervangen worden, met ongeveer één sensor per maand.
Omdat temperatuur en vochtigheid kritisch zijn voor de levenscyclus van de zwarte soldaatvlieg, creëerden sensorfouten een significant bedrijfsrisico—resulterend in productieverliezen en tegenslagen voor lopende R\&D-inspanningen.
Protix had behoefte aan een betrouwbaar, flexibel, cloud-enabled monitoringsysteem dat elk type LoRaWAN-sensor kon ondersteunen, om productiecontinuïteit en schaalbaarheid te garanderen.
## Onze Oplossing
Forrict implementeerde een moderne, serverless IoT data pipeline op AWS. De oplossing werd eerst bewezen door een proof of concept met Dragino LoRaWAN sensoren en gateways die direct verbinden met AWS IoT Core.
### Architectuur
**Data Ingestie:**
* Dragino LoRaWAN sensoren en gateways
* Directe verbinding met AWS IoT Core
* Open architectuur elimineert vendor lock-in
**Data Verwerking:**
* AWS IoT Rules voor message routing
* AWS Lambda voor payload decoding
* Flexibele pipeline voor elk sensortype
**Data Opslag:**
* Amazon Timestream voor time-series data
* Serverless, schaalbaar, laag onderhoud
* Tot 1 jaar data retentie
**Visualisatie:**
* Amazon Managed Grafana dashboards
* Real-time monitoring
* Historische trendanalyse
### Belangrijke Ontwerpprincipes
De architectuur is ontworpen voor eenvoudige uitbreiding—nieuwe sensoren kunnen worden toegevoegd zonder de oplossing te herontwerpen. Het systeem ondersteunt momenteel twee sensortypes, met meer gepland voor toekomstige uitrol.
Forrict beheert de end-to-end oplossing namens Protix, waardoor operationele continuïteit en minimale onderhoudsoverhead wordt gegarandeerd. Protix behoudt de mogelijkheid om kleine aanpassingen te maken, zoals het onboarden van nieuwe sensoren, terwijl Forrict voortdurende monitoring, updates en optimalisatie verzorgt.
## Resultaten en Voordelen
De AWS-gebaseerde oplossing heeft de productiemonitoring van Protix getransformeerd en levert zowel operationele stabiliteit als bedrijfswaarde:
### Operationele Verbeteringen
* **Sensor uptime:** Verhoogd van 1 maand naar 5-7 jaar dankzij langdurige LoRaWAN-apparaten met gemonitorde batterijstatus
* **Sensor onboarding:** Teruggebracht naar 15 minuten, wat snelle uitbreiding over faciliteiten mogelijk maakt
* **Onderhoud:** Vrijwel onderhoudsvrij door serverless architectuur
### Kostenbesparingen
* **50% lagere meetkosten:** Sensoren maken nu meerdere metingen per apparaat mogelijk, wat de kosten per meting verlaagt ten opzichte van het legacy systeem
### Verbeterde Mogelijkheden
* **Gecentraliseerde dashboards:** Zichtbaarheid over alle faciliteiten vanaf elke locatie
* **Historische data:** 1 jaar retentie ondersteunt productieanalyse en R\&D
* **Verminderd downtime risico:** Proactief onderhoud door betrouwbare monitoring
### Toekomstige Verbeteringen
* Single sign-on (SSO) integratie
* Geautomatiseerde alerts en notificaties
## Gebruikte Technologieën
* **AWS Services:** AWS IoT Core, AWS Lambda, Amazon Timestream, Amazon Managed Grafana, AWS IoT Rules
* **Hardware:** Dragino LoRaWAN sensoren en gateways
* **Protocol:** LoRaWAN
***
**Download de volledige case study:** [Protix AWS IoT Case Study (PDF)](/downloads/protix-aws-iot-case-study.pdf)
**Wil je vergelijkbare resultaten voor jouw IoT-project?** [Neem contact op](/nl/about) om je wensen te bespreken.
### Tags
IoT AWS IoT Core Serverless AgriTech LoRaWAN
## Klaar voor Jouw Succesverhaal?
Laten we bespreken hoe we jou kunnen helpen vergelijkbare resultaten te bereiken
[Bekijk Alle Case Studies ](/nl/case-studies)
[ Neem Contact Op](mailto:info@forrict.nl)
---
# Cookiebeleid
> Dit Cookiebeleid legt uit hoe Forrict cookies en vergelijkbare technologieën gebruikt op onze website www.forrict.nl. Door onze website te gebruiken, gaat
Laatst bijgewerkt: januari 2025
Dit Cookiebeleid legt uit hoe Forrict cookies en vergelijkbare technologieën gebruikt op onze website www\.forrict.nl. Door onze website te gebruiken, gaat u akkoord met het gebruik van cookies zoals beschreven in dit beleid.
## Wat Zijn Cookies?
Cookies zijn kleine tekstbestanden die op uw apparaat worden opgeslagen wanneer u een website bezoekt. Ze helpen de website uw voorkeuren te onthouden en uw browse-ervaring te verbeteren.
## Hoe Wij Cookies Gebruiken
Wij gebruiken cookies voor de volgende doeleinden:
* **Essentiële cookies:** Vereist voor de goede werking van de website
* **Analytische cookies:** Om te begrijpen hoe bezoekers onze website gebruiken
* **Marketing cookies:** Om relevante advertenties te leveren en campagneprestaties te volgen
## Cookies Die Wij Gebruiken
| Cookienaam | Doel | Type | Duur |
| ------------------------ | ------------------------------------------ | ------------ | --------- |
| forrict\_cookie\_consent | Slaat uw cookietoestemming voorkeuren op | Noodzakelijk | 1 jaar |
| \_ga | Google Analytics - onderscheidt gebruikers | Analytisch | 2 jaar |
| \_ga\_\* | Google Analytics - slaat sessiestatus op | Analytisch | 2 jaar |
| \_gid | Google Analytics - onderscheidt gebruikers | Analytisch | 24 uur |
| li\_fat\_id | LinkedIn Insight Tag - conversietracking | Marketing | 30 dagen |
| \_gcl\_au | Google Ads - conversietracking | Marketing | 3 maanden |
## Cookies van Derden
Wij gebruiken de volgende diensten van derden die cookies kunnen plaatsen:
### Google Analytics
Om websiteverkeer en gebruikersgedrag te analyseren. Voor meer informatie, zie het Privacybeleid van Google. [Learn more →](https://policies.google.com/privacy)
### Google Tag Manager
Om marketing tags te beheren en implementeren zonder code te wijzigen. [Learn more →](https://policies.google.com/privacy)
### LinkedIn Insight Tag
Om conversies te volgen en advertenties te targeten. Voor meer informatie, zie het Cookiebeleid van LinkedIn. [Learn more →](https://www.linkedin.com/legal/cookie-policy)
## Hoe Cookies Te Beheren
U kunt cookies op verschillende manieren beheren:
* **Cookiebanner:** Gebruik onze cookiebanner om niet-essentiële cookies te accepteren of te weigeren
* **Browserinstellingen:** De meeste browsers staan u toe cookies te weigeren of te verwijderen. Instructies verschillen per browser
* **Opt-out Tools:** Gebruik tools zoals [Google Analytics Opt-out Browser Add-on](https://tools.google.com/dlpage/gaoptout)
Let op: Het uitschakelen van noodzakelijke cookies kan de functionaliteit van onze website beïnvloeden.
## Google Consent Mode v2
Wij gebruiken Google Consent Mode v2 om uw privacykeuzes te respecteren. Dit betekent dat analytische en marketing cookies alleen laden nadat u toestemming heeft gegeven.
## Gegevensbewaring
* Analysegegevens worden 14 maanden bewaard
* Cookietoestemmingsvoorkeuren worden 1 jaar opgeslagen
* Marketing cookies verlopen na 30-90 dagen afhankelijk van het platform
## Wijzigingen in Dit Beleid
Wij kunnen dit Cookiebeleid van tijd tot tijd bijwerken. De datum "Laatst bijgewerkt" bovenaan geeft aan wanneer wijzigingen voor het laatst zijn aangebracht.
## Contact
Als u vragen heeft over ons gebruik van cookies, neem dan contact met ons op:
**Email:**
**Address:** Waspikseweg 25, 5109PE 's-Gravenmoer, Nederland
---
# We Helpen Bedrijven met Cloud
> Ontdek hoe Forrict bedrijven helpt succes te behalen met AWS.
Forrict helpt jouw bedrijf vooruit met Amazon Web Services (AWS). Dankzij onze expertise en brede AWS-diensten stimuleren we innovatie, verbeteren we efficiëntie en ondersteunen we je groei.
### Onze principes
Onze principes zijn geen posters aan de muur ze bepalen hoe wij elke dag echte waarde leveren. En omdat we ze toepassen vanaf het allereerste gesprek tot en met de uiteindelijke overdracht, voelt samenwerken met Forrict helder, samenwerkend en verfrissend voorspelbaar. Zo ziet dat er in de praktijk uit.
1
### Cloud Strategie en Planning
We beginnen met het begrijpen van jouw unieke doelen en IT-landschap. Op basis daarvan ontwikkelen we samen een op maat gemaakte cloudstrategie en roadmap die technologie naadloos koppelt aan bedrijfsdoelstellingen.
2
### AWS Migratie Services
Forrict plant en realiseert soepele migraties naar AWS, met minimale downtime. We optimaliseren workloads direct voor prestaties en kostenefficiëntie.
3
### Cloud Architectuur en Design
Onze AWS-gecertificeerde architecten ontwikkelen schaalbare, veilige en kosteneffectieve omgevingen. We kiezen de juiste AWS-diensten, implementeren best practices en zorgen voor hoge beschikbaarheid en disaster recovery.
4
### Security en Compliance
Security staat voorop. We helpen bij identity & access management, encryptie, monitoring en compliance (waaronder AVG/GDPR), zodat jouw data beschermd blijft en risico's beperkt worden.
### The Forrict Way of Working
Met onze aanpak geeft jou controle en je tegelijk toegang tot diepgaande AWS-expertise en beproefd vakmanschap. Of je ons nu hands-on, hands-off of ergens daartussen wilt inzetten, het doel is altijd hetzelfde: je team helpen sneller, veiliger en slimmer te werken zonder afhankelijkheid te creëren.
1
### Kostenoptimalisatie
We monitoren gebruik, identificeren besparingen en implementeren strategieën om kosten te beheersen. Zo haal je maximale waarde uit je investering.
2
### DevOps en Automatisering
We versnellen ontwikkeling en innovatie met DevOps, CI/CD en Infrastructure as Code. Dit zorgt voor snellere releases, meer wendbaarheid en hogere kwaliteit.
3
### Managed Services en Support
Forrict biedt doorlopende ondersteuning voor jouw AWS-omgeving, inclusief 24/7 monitoring, proactieve incidentafhandeling en performance-beheer.
4
### Training en Vaardigheidsontwikkeling
We versterken jouw teams met trainingen en certificeringstrajecten, zodat ze zelfstandig en effectief kunnen werken in de cloud.
5
### Cloud Innovatie en Schaalbaarheid
We helpen klanten nieuwe mogelijkheden te benutten met o.a. machine learning, AI, IoT en serverless computing. Zo bouw je aan een toekomstbestendige en schaalbare cloudomgeving.
## Wat je van ons mag verwachten
Forrict staat naast je als strategische AWS-partner. We begeleiden je door elke stap van je cloudreis, optimaliseren jouw AWS-omgeving en versterken je security-positie. We zorgen dat je het maximale uit AWS haalt — afgestemd op jouw doelen, jouw tempo en jouw manier van werken. Zo helpen we je niet alleen om resultaten te behalen, maar ook om duurzaam succes op te bouwen.
[ Start Je Transformatie ](mailto:info@forrict.nl)
[Lees Onze Blog](/nl/blog)
---
# Blijf op de hoogte
> Schrijf je in voor praktische AWS-tips, cloud-kosteninzichten en beveiligingsadvies, direct in je inbox. Geen spam, je kunt je altijd uitschrijven.
Schrijf je in voor praktische AWS-tips, cloud-kosteninzichten en beveiligingsadvies, direct in je inbox. Geen spam, je kunt je altijd uitschrijven.
### Blijf op de hoogte
Ontvang AWS-inzichten en tips in je inbox.
Voornaam (optioneel)[Jouw e-mailadres]()Aanmelden
---
# Privacybeleid
> Forrict ("wij", "ons" of "onze") respecteert uw privacy en zet zich in voor de bescherming van uw persoonlijke gegevens. Dit privacybeleid legt uit hoe wij
Laatst bijgewerkt: januari 2025
Forrict ("wij", "ons" of "onze") respecteert uw privacy en zet zich in voor de bescherming van uw persoonlijke gegevens. Dit privacybeleid legt uit hoe wij uw informatie verzamelen, gebruiken en beschermen wanneer u onze website www\.forrict.nl bezoekt.
## 1. Informatie Die Wij Verzamelen
* **Informatie die u verstrekt:** Wanneer u contact met ons opneemt of formulieren op onze website invult, kunnen wij uw naam, e-mailadres, bedrijfsnaam en andere informatie die u verstrekt verzamelen.
* **Automatisch verzamelde informatie:** Wij verzamelen technische informatie zoals uw IP-adres, browsertype, apparaatinformatie en hoe u omgaat met onze website via cookies en vergelijkbare technologieën.
* **Analysegegevens:** Met uw toestemming gebruiken wij Google Analytics om te begrijpen hoe bezoekers onze website gebruiken.
## 2. Hoe Wij Uw Informatie Gebruiken
* Om te reageren op uw vragen en klantenondersteuning te bieden
* Om onze website en diensten te verbeteren
* Om websitegebruik en -prestaties te analyseren
* Om u marketingcommunicatie te sturen (met uw toestemming)
* Om te voldoen aan wettelijke verplichtingen
## 3. Rechtsgrondslag voor Verwerking (AVG)
* **Toestemming:** Wanneer u toestemming geeft voor marketingcommunicatie of analytische cookies
* **Gerechtvaardigde belangen:** Voor het verbeteren van onze diensten en websitefunctionaliteit
* **Contractuitvoering:** Wanneer nodig om onze diensten te leveren
* **Wettelijke naleving:** Wanneer vereist door de wet
## 4. Gegevensdeling en Derden
* Wij verkopen uw persoonlijke gegevens niet. Wij kunnen uw informatie delen met:
* **Dienstverleners:** Google Analytics (analyse), Google Tag Manager (tagbeheer), LinkedIn (marketing, met uw toestemming)
* **Wettelijke vereisten:** Wanneer vereist door de wet of om onze rechten te beschermen
## 5. Uw Rechten Onder de AVG
* **Recht op toegang:** Vraag een kopie van uw persoonlijke gegevens aan
* **Recht op rectificatie:** Corrigeer onjuiste persoonlijke gegevens
* **Recht op gegevenswissing:** Vraag verwijdering van uw persoonlijke gegevens aan
* **Recht op beperking:** Beperk hoe wij uw gegevens gebruiken
* **Recht op gegevensoverdraagbaarheid:** Ontvang uw gegevens in een gestructureerd formaat
* **Recht van bezwaar:** Maak bezwaar tegen verwerking van uw persoonlijke gegevens
* **Recht om toestemming in te trekken:** Trek toestemming op elk moment in
* Om deze rechten uit te oefenen, neem contact met ons op via info\@forrict.nl
## 6. Gegevensbewaring
* Wij bewaren uw persoonlijke gegevens alleen zolang als nodig is voor de doeleinden die in dit beleid worden beschreven of zoals vereist door de wet. Analysegegevens worden 14 maanden bewaard.
## 7. Gegevensbeveiliging
* Wij implementeren passende technische en organisatorische maatregelen om uw persoonlijke gegevens te beschermen tegen ongeautoriseerde toegang, wijziging, openbaarmaking of vernietiging.
## 8. Cookies
* Wij gebruiken cookies en vergelijkbare technologieën. Voor gedetailleerde informatie over de cookies die wij gebruiken, zie ons [Cookiebeleid](/nl/cookie-policy).
## 9. Internationale Gegevensoverdrachten
* Uw gegevens kunnen worden overgedragen naar en verwerkt in landen buiten de Europese Economische Ruimte (EER). Wij zorgen ervoor dat passende waarborgen aanwezig zijn, zoals standaard contractuele clausules.
## 10. Wijzigingen in Dit Beleid
* Wij kunnen dit privacybeleid van tijd tot tijd bijwerken. De datum "Laatst bijgewerkt" bovenaan geeft aan wanneer het beleid voor het laatst is herzien.
## 11. Contact
* Als u vragen heeft over dit privacybeleid of uw rechten wilt uitoefenen, neem dan contact met ons op:
* **E-mail:** info\@forrict.nl
* **Adres:** Waspikseweg 25, 5109PE 's-Gravenmoer, Nederland
---
# Onze Diensten
> Expert AWS consultancy diensten op maat gemaakt
1. [Home](/nl/)
2. /
3. Diensten
Expert AWS consultancy diensten op maat gemaakt
### FinOps & Cost Optimization
Grip op je AWS-kosten, zonder je snelheid te verliezen.
Cloud Consulting finops
[Meer informatie ](/nl/services/Finops)
### Flex consult
Voldoe aan je cloud behoeften met on-demand consultancy.
Cloud Consulting Flex-consulting
[Meer informatie ](/nl/services/Flex-consult)
### Security assessment
Versterk de security posture van je AWS infrastructuur
Cloud Consulting Security Review
[Meer informatie ](/nl/services/Security-assessment)
### Landingzones & Governance
Start secure. Scale without chaos.
Landingzone aws governance
[Meer informatie ](/nl/services/landingzones)
### Managed AWS
Beheerde AWS diensten voor efficiënte en veilige cloud operations
managed aws aws managed services
[Meer informatie ](/nl/services/managed-aws)
### Well architected review
Ontvang expert begeleiding over architectuur best practices door onze AWS Well-Architected review.
Cloud Consulting Well Architect Review
[Meer informatie ](/nl/services/well-architected-review)
## Klaar om je AWS Infrastructuur te Transformeren?
Laten we bespreken hoe we je cloud journey kunnen optimaliseren
[ Neem Contact Op ](mailto:info@forrict.nl)
[Hoe We Werken](/nl/how-we-work)
---
# FinOps & Cost Optimization
> Grip op je AWS-kosten, zonder je snelheid te verliezen.
AWS maakt snel schalen makkelijk, maar kosten kunnen net zo snel ontsporen. Forrict helpt teams hun cloudkosten begrijpen, sturen en voorspellen, zodat geld weer een hulpmiddel wordt in plaats van een verrassing.
## Waarom AWS-kosten vaak uit de hand lopen
Het ligt meestal niet aan één fout, maar aan een combinatie van:
* Snel groeiende workloads
* Gebrek aan inzicht per team of product
* Geen duidelijke afspraken over eigenaarschap
* Optimalisatie die te laat (of helemaal niet) gebeurt
Het resultaat: stijgende facturen en onrust terwijl niemand precies weet waar het geld naartoe gaat.
## FinOps volgens Forrict
Voor ons is FinOps geen tool, dashboard of finance-oefening. Het is een praktische manier van samenwerken tussen engineering, product en finance.
Wij helpen je om:
* inzicht te krijgen in waar je geld heen gaat
* kosten te koppelen aan teams en keuzes
* bewuste beslissingen te nemen over groei
* verspilling te verminderen zonder risico’s
Altijd transparant. Altijd samen.
## Wat dit oplevert
* Voorspelbare AWS-kosten
* Minder verspilling
* Meer vertrouwen bij finance en management
* Duidelijke inzichten voor teams
* Ruimte om te blijven innoveren
Kortom: controle zonder rem op groei.
### Klaar om te Beginnen?
Laten we jouw AWS project bespreken en hoe we je doelen kunnen helpen bereiken.
[Neem Contact Op ](mailto:info@forrict.nl)
[Hoe We Werken](/nl/how-we-work)
## Gerelateerde Diensten
### [Flex consult](/nl/services/Flex-consult)
[Voldoe aan je cloud behoeften met on-demand consultancy.](/nl/services/Flex-consult)
[Meer informatie →](/nl/services/Flex-consult)
### [Security assessment](/nl/services/Security-assessment)
[Versterk de security posture van je AWS infrastructuur](/nl/services/Security-assessment)
[Meer informatie →](/nl/services/Security-assessment)
### [Landingzones & Governance](/nl/services/landingzones)
[Start secure. Scale without chaos.](/nl/services/landingzones)
[Meer informatie →](/nl/services/landingzones)
## Klaar om je AWS Infrastructuur te Transformeren?
Laten we bespreken hoe we je cloud journey kunnen optimaliseren
[Neem Contact Op ](mailto:info@forrict.nl)
[Bekijk alle diensten](/nl/services)
---
# Flex consult
> Voldoe aan je cloud behoeften met on-demand consultancy.
Soms heb je geen volledig project of managed service nodig. Je hebt gewoon snel een helder antwoord nodig, een second opinion, of hands-on hulp. Flex Consult geeft je direct toegang tot ervaren AWS-experts, zonder contracten, verplichtingen of complexiteit.
## Wanneer Flex Consult een goede keuze is
Flex Consult werkt vooral goed als je:
* Nu meteen een AWS-vraag beantwoord wilt hebben
* Een snelle architectuurreview nodig hebt
* Een second opinion wilt vóórdat je een beslissing neemt
* Te maken hebt met een security- of kostenissue
* Hulp nodig hebt om je team weer vlot te trekken
* Expertise wilt zonder alles uit handen te geven
Korte feedbackloops. Duidelijke antwoorden. Geen overhead.
## Waar we bij helpen
Flex Consult kun je inzetten voor bijvoorbeeld:
* Architectuurreviews en ontwerpkeuzes
* Security- en compliance-vraagstukken
* Kosten- en FinOps-reviews
* Advies over AWS-accounts en landing zones
* CI/CD- en infrastructuurinrichting
* Incidentreviews en troubleshooting
* Schaalbaarheids- en performancevragen
Raakt het AWS? Dan kunnen wij helpen.
## Hoe het werkt
1. Jij boekt tijd wanneer jij die nodig hebt
2. Wij schuiven remote aan, gefocust en voorbereid
3. We werken live samen
4. Jij vertrekt met helderheid, vervolgstappen en volledige eigenaarschap
Geen rapporten die je niet leest. Geen vage adviezen. Gewoon praktische hulp waar je direct mee aan de slag kunt.
## Wat je krijgt
* Directe toegang tot senior AWS-expertise
* Heldere en eerlijke antwoorden
* Praktische begeleiding afgestemd op jouw omgeving
* Volledige transparantie in alles wat we doen
* Kennis die je binnen je eigen team kunt hergebruiken
Nu AWS-hulp nodig? Of het nu om één uur gaat of om een paar sessies: Flex Consult past zich aan jouw behoeften aan.
### Klaar om te Beginnen?
Laten we jouw AWS project bespreken en hoe we je doelen kunnen helpen bereiken.
[Neem Contact Op ](mailto:info@forrict.nl)
[Hoe We Werken](/nl/how-we-work)
## Gerelateerde Diensten
### [FinOps & Cost Optimization](/nl/services/Finops)
[Grip op je AWS-kosten, zonder je snelheid te verliezen.](/nl/services/Finops)
[Meer informatie →](/nl/services/Finops)
### [Security assessment](/nl/services/Security-assessment)
[Versterk de security posture van je AWS infrastructuur](/nl/services/Security-assessment)
[Meer informatie →](/nl/services/Security-assessment)
### [Landingzones & Governance](/nl/services/landingzones)
[Start secure. Scale without chaos.](/nl/services/landingzones)
[Meer informatie →](/nl/services/landingzones)
## Klaar om je AWS Infrastructuur te Transformeren?
Laten we bespreken hoe we je cloud journey kunnen optimaliseren
[Neem Contact Op ](mailto:info@forrict.nl)
[Bekijk alle diensten](/nl/services)
---
# Landingzones & Governance
> Start secure. Scale without chaos.
Je eerste architectuurkeuzes op AWS hebben impact op de lange termijn. Een goed ontworpen landing zone geeft je team een veilige, schaalbare basis en voorkomt dat complexiteit langzaam binnensluipt naarmate je groeit.
Forrict helpt je bij het bouwen van AWS-fundamenten die helder, voorspelbaar en volledig onder jouw controle zijn.
## Waarom landing zones belangrijk zijn
Zonder een solide basis groeien AWS-omgevingen vaak organisch en onvoorspelbaar. Accounts vermenigvuldigen zich, permissies gaan schuiven, kosten worden lastiger te volgen en security-maatregelen verzwakken langzaam.
Een sterke landing zone helpt je om:
* veilig te schalen over teams en omgevingen
* security- en compliance-risico’s te verkleinen
* kosten inzichtelijk en voorspelbaar te houden
* herwerk later te voorkomen
Het is veel eenvoudiger om dit vanaf het begin goed neer te zetten dan het achteraf te moeten repareren.
## Wat een Forrict landing zone omvat
Elke landing zone is maatwerk, maar bevat meestal:
* Een multi-accountstructuur met duidelijke scheiding
* Gecentraliseerd identity- en accessmanagement (IAM)
* Netwerkontwerp en segmentatie
* Logging, monitoring en audit trails
* Security-baselines en guardrails
* Kosteninzicht en accountstructuur
* Automatisering voor account provisioning
* Alles gebouwd volgens AWS best practices en services
## Governance zonder bureaucratie
Governance hoeft teams niet af te remmen. Bij Forrict betekent governance het neerzetten van duidelijke kaders die teams juist sneller en veiliger laten werken — niet het toevoegen van extra goedkeuringslagen.
Wij focussen op:
* Guardrails in plaats van handmatige controles
* Automatisering boven documentatie
* Duidelijk eigenaarschap en verantwoordelijkheden
* Zichtbaarheid in plaats van beperking
Zo weet iedereen wat wel kan, wat niet, en waarom.
## Hoe we dit samen opbouwen
1. Begrijpen van jullie context Jullie teams, workloads, risico’s en groeiplannen.
2. Ontwerpen van de basis Een heldere architectuur die past bij jullie organisatie — geen generiek template.
3. Open bouwen Alles is gedocumenteerd, toegelicht en inzichtelijk.
4. Jullie team in staat stellen We zorgen dat jullie team de setup begrijpt en er met vertrouwen mee kan werken.
Geen black boxes. Geen vendor lock-in.
## Wat je krijgt
* Een veilige en schaalbare AWS-fundering
* Heldere account- en permissiestructuren
* Sterke security- en compliance-baselines
* Eenvoudiger beheer en betere kostencontrole
* Een setup die je team écht begrijpt
Je bent klaar om te groeien, zonder de controle te verliezen.
## Wanneer dit waardevol is
Landing Zones & Governance zijn vooral zinvol als je:
* Net start met AWS
* Groeit voorbij één enkele AWS-account
* Betere security- of compliance-maatregelen nodig hebt
* Wilt standaardiseren over teams heen
* Klaar bent met het steeds opnieuw oplossen van fundamentele problemen
## Klaar om je AWS-fundament te bouwen?
Laten we een landing zone ontwerpen die je groei ondersteunt — nu en in de toekomst.
### Klaar om te Beginnen?
Laten we jouw AWS project bespreken en hoe we je doelen kunnen helpen bereiken.
[Neem Contact Op ](mailto:info@forrict.nl)
[Hoe We Werken](/nl/how-we-work)
## Gerelateerde Diensten
### [FinOps & Cost Optimization](/nl/services/Finops)
[Grip op je AWS-kosten, zonder je snelheid te verliezen.](/nl/services/Finops)
[Meer informatie →](/nl/services/Finops)
### [Flex consult](/nl/services/Flex-consult)
[Voldoe aan je cloud behoeften met on-demand consultancy.](/nl/services/Flex-consult)
[Meer informatie →](/nl/services/Flex-consult)
### [Security assessment](/nl/services/Security-assessment)
[Versterk de security posture van je AWS infrastructuur](/nl/services/Security-assessment)
[Meer informatie →](/nl/services/Security-assessment)
## Klaar om je AWS Infrastructuur te Transformeren?
Laten we bespreken hoe we je cloud journey kunnen optimaliseren
[Neem Contact Op ](mailto:info@forrict.nl)
[Bekijk alle diensten](/nl/services)
---
# Managed AWS
> Beheerde AWS diensten voor efficiënte en veilige cloud operations
Het draaien van productie-workloads op AWS vraagt focus, discipline en constante aandacht. Forrict helpt teams hun AWS-omgevingen stabiel, veilig en voorspelbaar te houden — zonder operations te veranderen in een black box.
Jij blijft aan het stuur. Wij zorgen dat alles soepel blijft draaien.
## Wanneer Managed AWS logisch is
Managed AWS is een goede keuze als:
* Je platform groeit en betrouwbare operations nodig heeft
* Je team minder operationele afleiding wil
* Je zekerheid wilt over beschikbaarheid, security en updates
* Je (nog) geen volledig ops-team wilt opbouwen
* Je wél zicht en controle over je cloud wilt houden
## Hoe wij AWS anders beheren
Managed AWS bij Forrict is gebaseerd op een paar simpele principes:
* Transparantie als standaard: je ziet wat we doen en waarom
* Gedeeld eigenaarschap: we werken mét je team, niet eromheen
* Geen lock-in: alles is gedocumenteerd en toegankelijk
* Voorspelbare operations: geen verrassingen, geen verborgen wijzigingen
Wij “nemen je cloud niet over”. We helpen je om ’m beter te runnen.
## Wat wij oppakken
Afhankelijk van jullie setup kan Managed AWS bestaan uit:
* Monitoring en alerting
* Incidentrespons en troubleshooting
* Security-updates en patching
* Backup- en recoveryprocessen
* AWS-service-updates en best practices
* Doorlopende verbeteringen aan betrouwbaarheid en performance
Alle wijzigingen worden besproken, vastgelegd en zijn zichtbaar.
## Wat je krijgt
* Een stabiele en betrouwbare AWS-omgeving
* Minder incidenten en minder operationele ruis
* Helder inzicht in wat er draait en waarom
* Meer vertrouwen bij je team en stakeholders
* Meer tijd om te focussen op het bouwen van je product
Operations worden voorspelbaar, niet stressvol.
## Voor wie dit bedoeld is
Managed AWS werkt het beste voor teams die:
* Productie-workloads op AWS draaien
* Security en betrouwbaarheid belangrijk vinden
* Operationele ondersteuning willen zonder de controle te verliezen
* Samenwerking verkiezen boven uitbesteding
## Klaar voor rustigere AWS-operations?
Laten we je AWS-omgeving betrouwbaar, voorspelbaar en prettig om mee te werken maken.
### Klaar om te Beginnen?
Laten we jouw AWS project bespreken en hoe we je doelen kunnen helpen bereiken.
[Neem Contact Op ](mailto:info@forrict.nl)
[Hoe We Werken](/nl/how-we-work)
## Gerelateerde Diensten
### [FinOps & Cost Optimization](/nl/services/Finops)
[Grip op je AWS-kosten, zonder je snelheid te verliezen.](/nl/services/Finops)
[Meer informatie →](/nl/services/Finops)
### [Flex consult](/nl/services/Flex-consult)
[Voldoe aan je cloud behoeften met on-demand consultancy.](/nl/services/Flex-consult)
[Meer informatie →](/nl/services/Flex-consult)
### [Security assessment](/nl/services/Security-assessment)
[Versterk de security posture van je AWS infrastructuur](/nl/services/Security-assessment)
[Meer informatie →](/nl/services/Security-assessment)
## Klaar om je AWS Infrastructuur te Transformeren?
Laten we bespreken hoe we je cloud journey kunnen optimaliseren
[Neem Contact Op ](mailto:info@forrict.nl)
[Bekijk alle diensten](/nl/services)
---
# Security assessment
> Versterk de security posture van je AWS infrastructuur
Security hoeft niet vaag, overweldigend of puur compliance-gedreven te voelen. Forrict helpt teams hun AWS-securitypositie te begrijpen, echte risico’s te identificeren en stap voor stap te verbeteren — zonder development te vertragen.
## Waarom security assessments belangrijk zijn
Naarmate AWS-omgevingen groeien, groeien securityrisico’s vaak ongemerkt mee. Misconfiguraties, ontbrekende controles en onduidelijke verantwoordelijkheden kunnen risico introduceren zonder dat iemand het doorheeft.
Een gerichte security assessment helpt je om:
* te begrijpen waar je vandaag staat
* echte risico’s vroegtijdig te signaleren
* verbeteringen te prioriteren
* vertrouwen te creëren bij stakeholders
Niet om met vingers te wijzen, maar om veilig vooruit te kunnen.
## Wat we beoordelen
Onze security assessments richten zich op de onderdelen die er écht toe doen binnen AWS, waaronder:
* Identity & Access Management (IAM)
* Netwerksecurity en segmentatie
* Logging, monitoring en detectie
* Databescherming en encryptie
* Isolatie van accounts en omgevingen
* Security guardrails en policies
Altijd afgestemd op jullie setup en risicoprofiel.
## Hoe de assessment werkt
1. Scope & context We stemmen af op jullie omgeving, doelen en randvoorwaarden.
2. Review & analyse We beoordelen jullie AWS-setup op basis van AWS best practices en praktijkervaring.
3. Heldere bevindingen Je krijgt een scherp overzicht van risico’s, hiaten en prioriteiten — zonder ruis.
4. Praktische aanbevelingen Concrete acties die je team daadwerkelijk kan uitvoeren.
Dit is een samenwerkingsproces, geen audit-verhoor.
## Wat je krijgt
* Helder inzicht in je huidige securitypositie
* Een geprioriteerde lijst met verbeterpunten
* Praktische aanbevelingen, geen theorie
* Gedeeld begrip binnen teams
* Een sterkere en veerkrachtigere AWS-omgeving
Security wordt iets wat je begrijpt, niet iets waar je bang voor bent.
## Wanneer dit waardevol is
Een security assessment is vooral zinvol als:
* Je AWS-omgeving snel is gegroeid
* Je je voorbereidt op audits of certificeringen
* Je risico wilt verkleinen zonder delivery te vertragen
* Je twijfelt of de huidige controles voldoende zijn
* Je een second opinion wilt van AWS-experts
## Meer duidelijkheid over je AWS-security?
Laten we samen rustig en scherp naar je omgeving kijken — en verbeteren wat er echt toe doet.
### Klaar om te Beginnen?
Laten we jouw AWS project bespreken en hoe we je doelen kunnen helpen bereiken.
[Neem Contact Op ](mailto:info@forrict.nl)
[Hoe We Werken](/nl/how-we-work)
## Gerelateerde Diensten
### [FinOps & Cost Optimization](/nl/services/Finops)
[Grip op je AWS-kosten, zonder je snelheid te verliezen.](/nl/services/Finops)
[Meer informatie →](/nl/services/Finops)
### [Flex consult](/nl/services/Flex-consult)
[Voldoe aan je cloud behoeften met on-demand consultancy.](/nl/services/Flex-consult)
[Meer informatie →](/nl/services/Flex-consult)
### [Landingzones & Governance](/nl/services/landingzones)
[Start secure. Scale without chaos.](/nl/services/landingzones)
[Meer informatie →](/nl/services/landingzones)
## Klaar om je AWS Infrastructuur te Transformeren?
Laten we bespreken hoe we je cloud journey kunnen optimaliseren
[Neem Contact Op ](mailto:info@forrict.nl)
[Bekijk alle diensten](/nl/services)
---
# Well architected review
> Ontvang expert begeleiding over architectuur best practices door onze AWS Well-Architected review.
AWS biedt krachtige bouwstenen, maar na verloop van tijd stapelen keuzes zich op. Een Well-Architected Review helpt je om even afstand te nemen, het grotere geheel te bekijken en je AWS-setup te verbeteren waar het er écht toe doet.
Tijdens de review beoordelen we de workload in je AWS-account grondig. Vervolgens ontvang je een gedetailleerd rapport waarin eventuele high-risk bevindingen uit de assessment worden uitgelicht. Daarnaast leveren we een op maat gemaakt verbeterplan om de geïdentificeerde issues aan te pakken en op te lossen, zodat je AWS-omgeving optimaal wordt ingericht en benut.
### Klaar om te Beginnen?
Laten we jouw AWS project bespreken en hoe we je doelen kunnen helpen bereiken.
[Neem Contact Op ](mailto:info@forrict.nl)
[Hoe We Werken](/nl/how-we-work)
## Gerelateerde Diensten
### [FinOps & Cost Optimization](/nl/services/Finops)
[Grip op je AWS-kosten, zonder je snelheid te verliezen.](/nl/services/Finops)
[Meer informatie →](/nl/services/Finops)
### [Flex consult](/nl/services/Flex-consult)
[Voldoe aan je cloud behoeften met on-demand consultancy.](/nl/services/Flex-consult)
[Meer informatie →](/nl/services/Flex-consult)
### [Security assessment](/nl/services/Security-assessment)
[Versterk de security posture van je AWS infrastructuur](/nl/services/Security-assessment)
[Meer informatie →](/nl/services/Security-assessment)
## Klaar om je AWS Infrastructuur te Transformeren?
Laten we bespreken hoe we je cloud journey kunnen optimaliseren
[Neem Contact Op ](mailto:info@forrict.nl)
[Bekijk alle diensten](/nl/services)